AI governance & NIS2in one software.
Two clearly separated modules on a shared foundation: the AI governance module for the EU AI Act and ISO/IEC 42001, and the NIS2 module for cybersecurity and business continuity.

AI governance
AI inventory, risk assessment, approvals and monitoring for the EU AI Act and ISO/IEC 42001 – in 6 areas.
Go to the AI governance moduleNIS2 & business continuity
From scoping and business impact to incidents, reporting deadlines and audit preparation.
Go to the NIS2 moduleOne software, one foundation
Both modules use the same core functions. If you manage AI governance and NIS2 together, you maintain roles, entities and deadlines only once.
Multi-tenant
Several entities in one software, with organisation switching for consultants.
Roles, permissions & 2FA
7 roles with a dedicated NIS2 permission and two-factor sign-in via authenticator app – optionally mandatory for the whole organisation.
Audit log
Extended log with filters, timeline and CSV export.
AI with transparency
Personal data is redacted before every AI call; suggestions show their rationale or confidence.
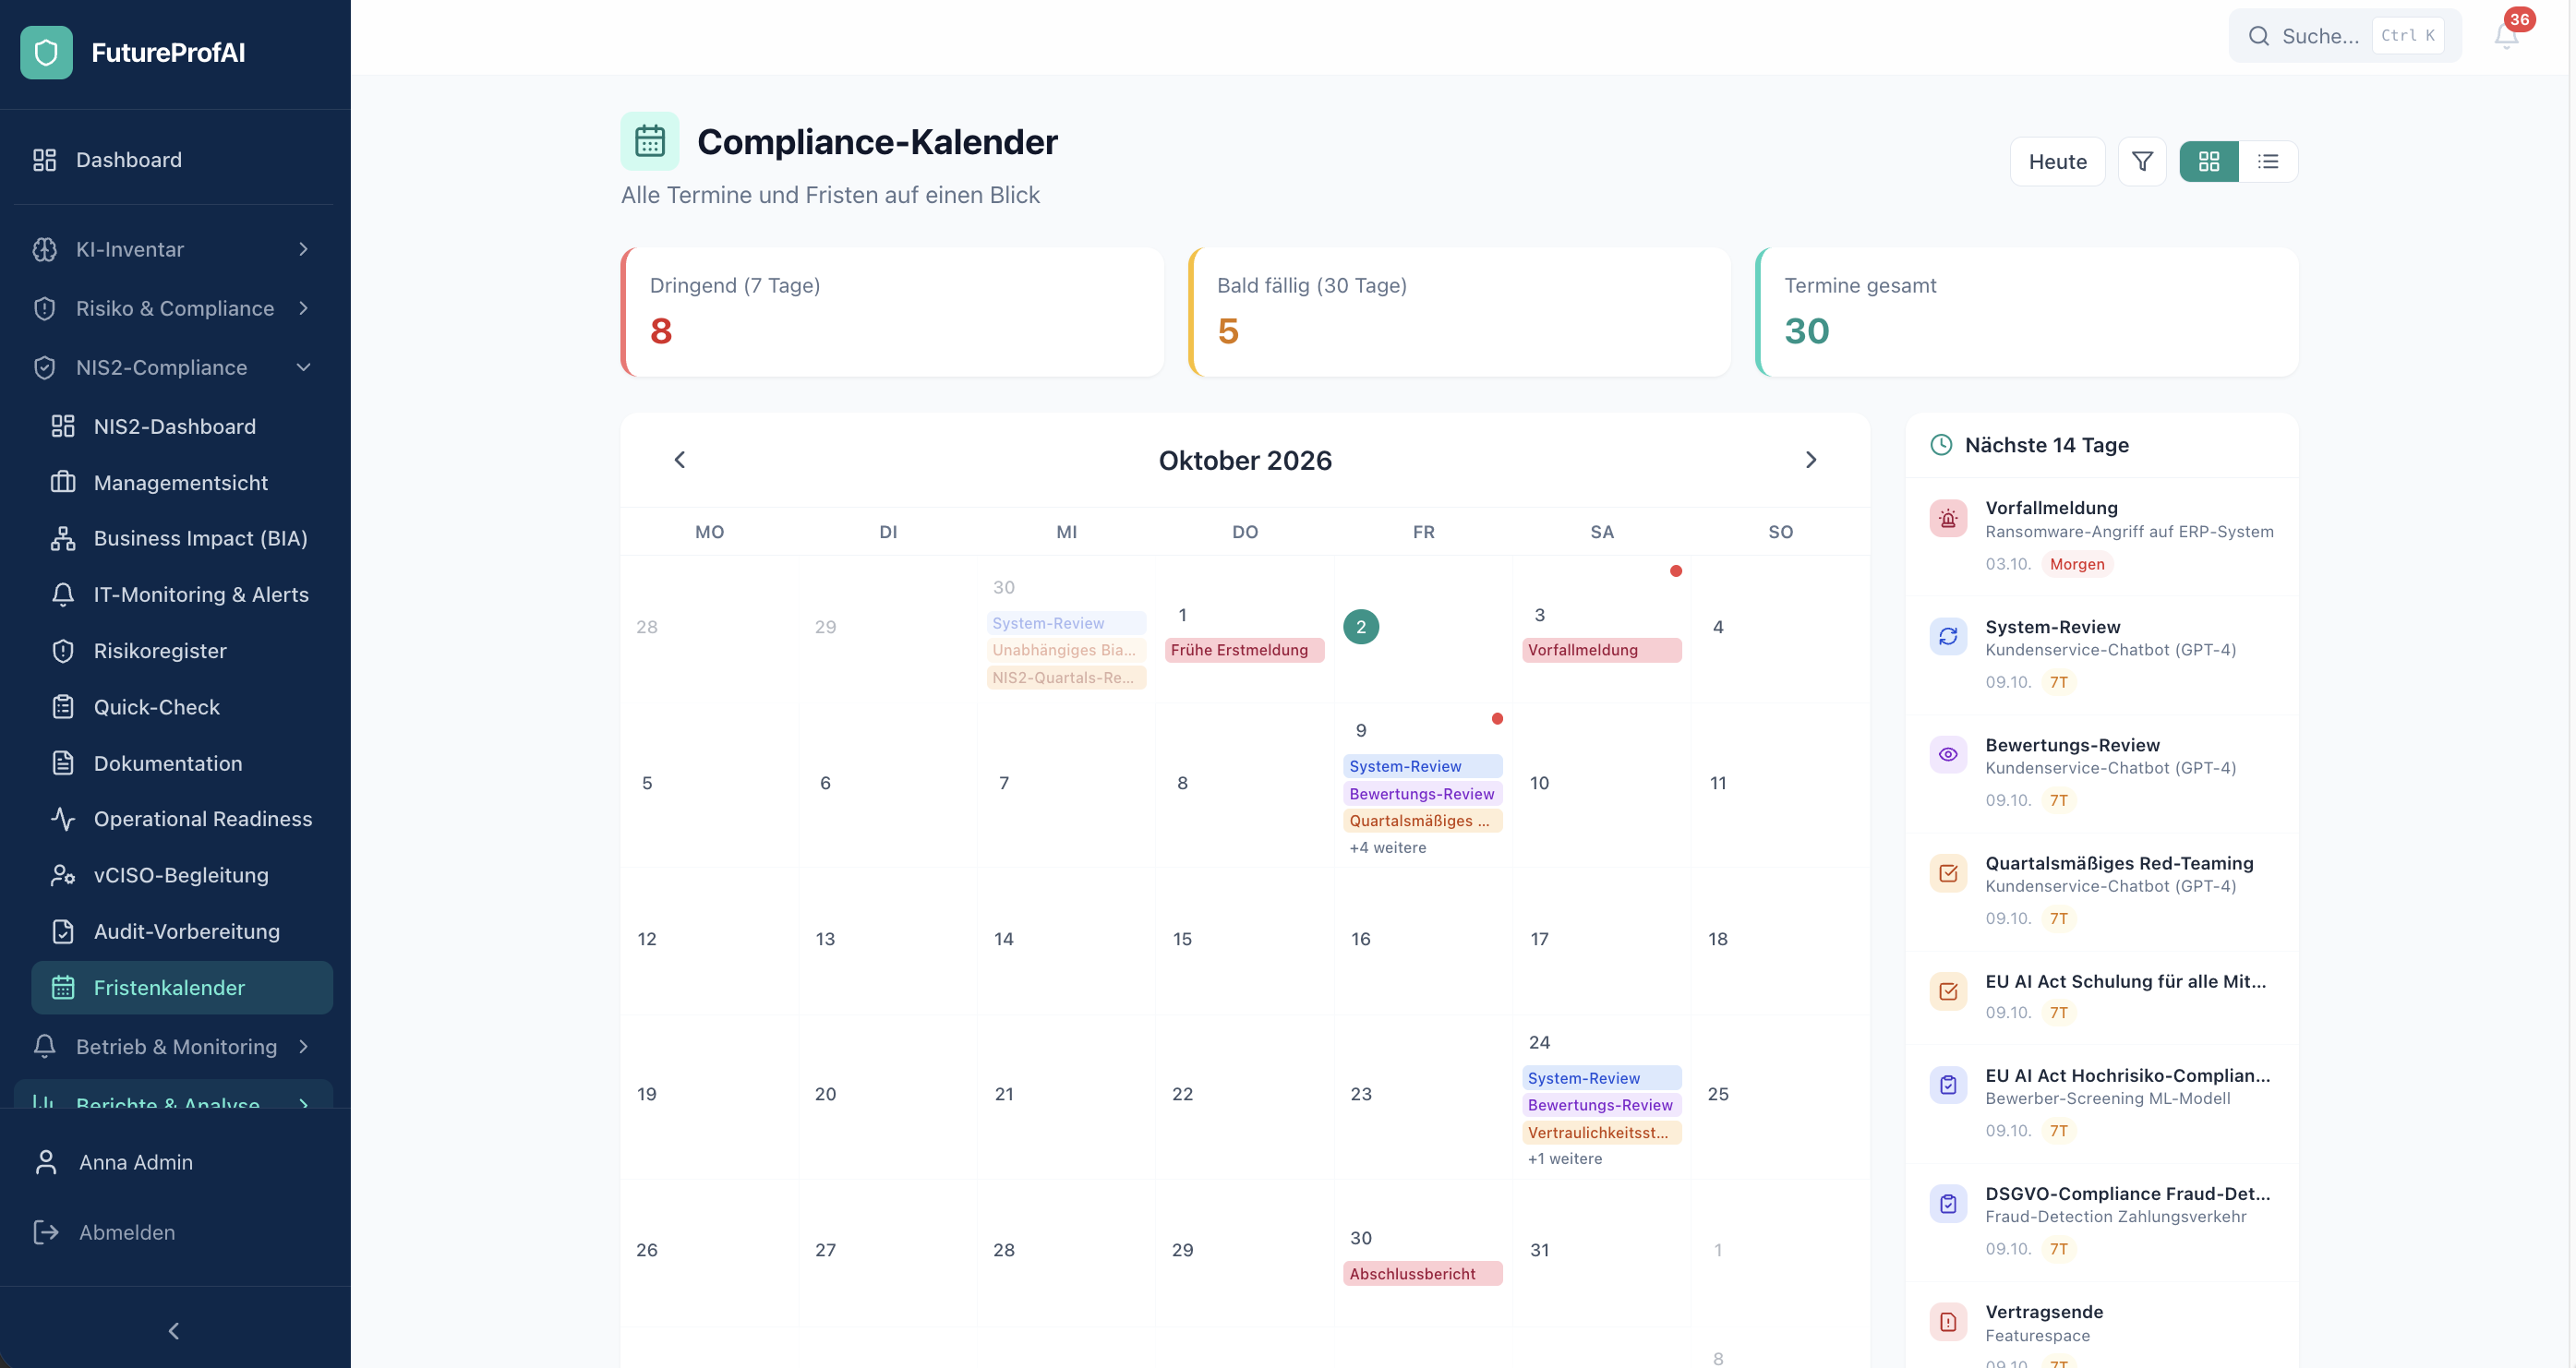
One calendar for all deadlines
AI reviews, NIS2 reporting deadlines, document reviews and audits in one compliance calendar.
Reports & notifications
Management reports as PDF, notifications via bell and email.
From the AI system to the audit evidence
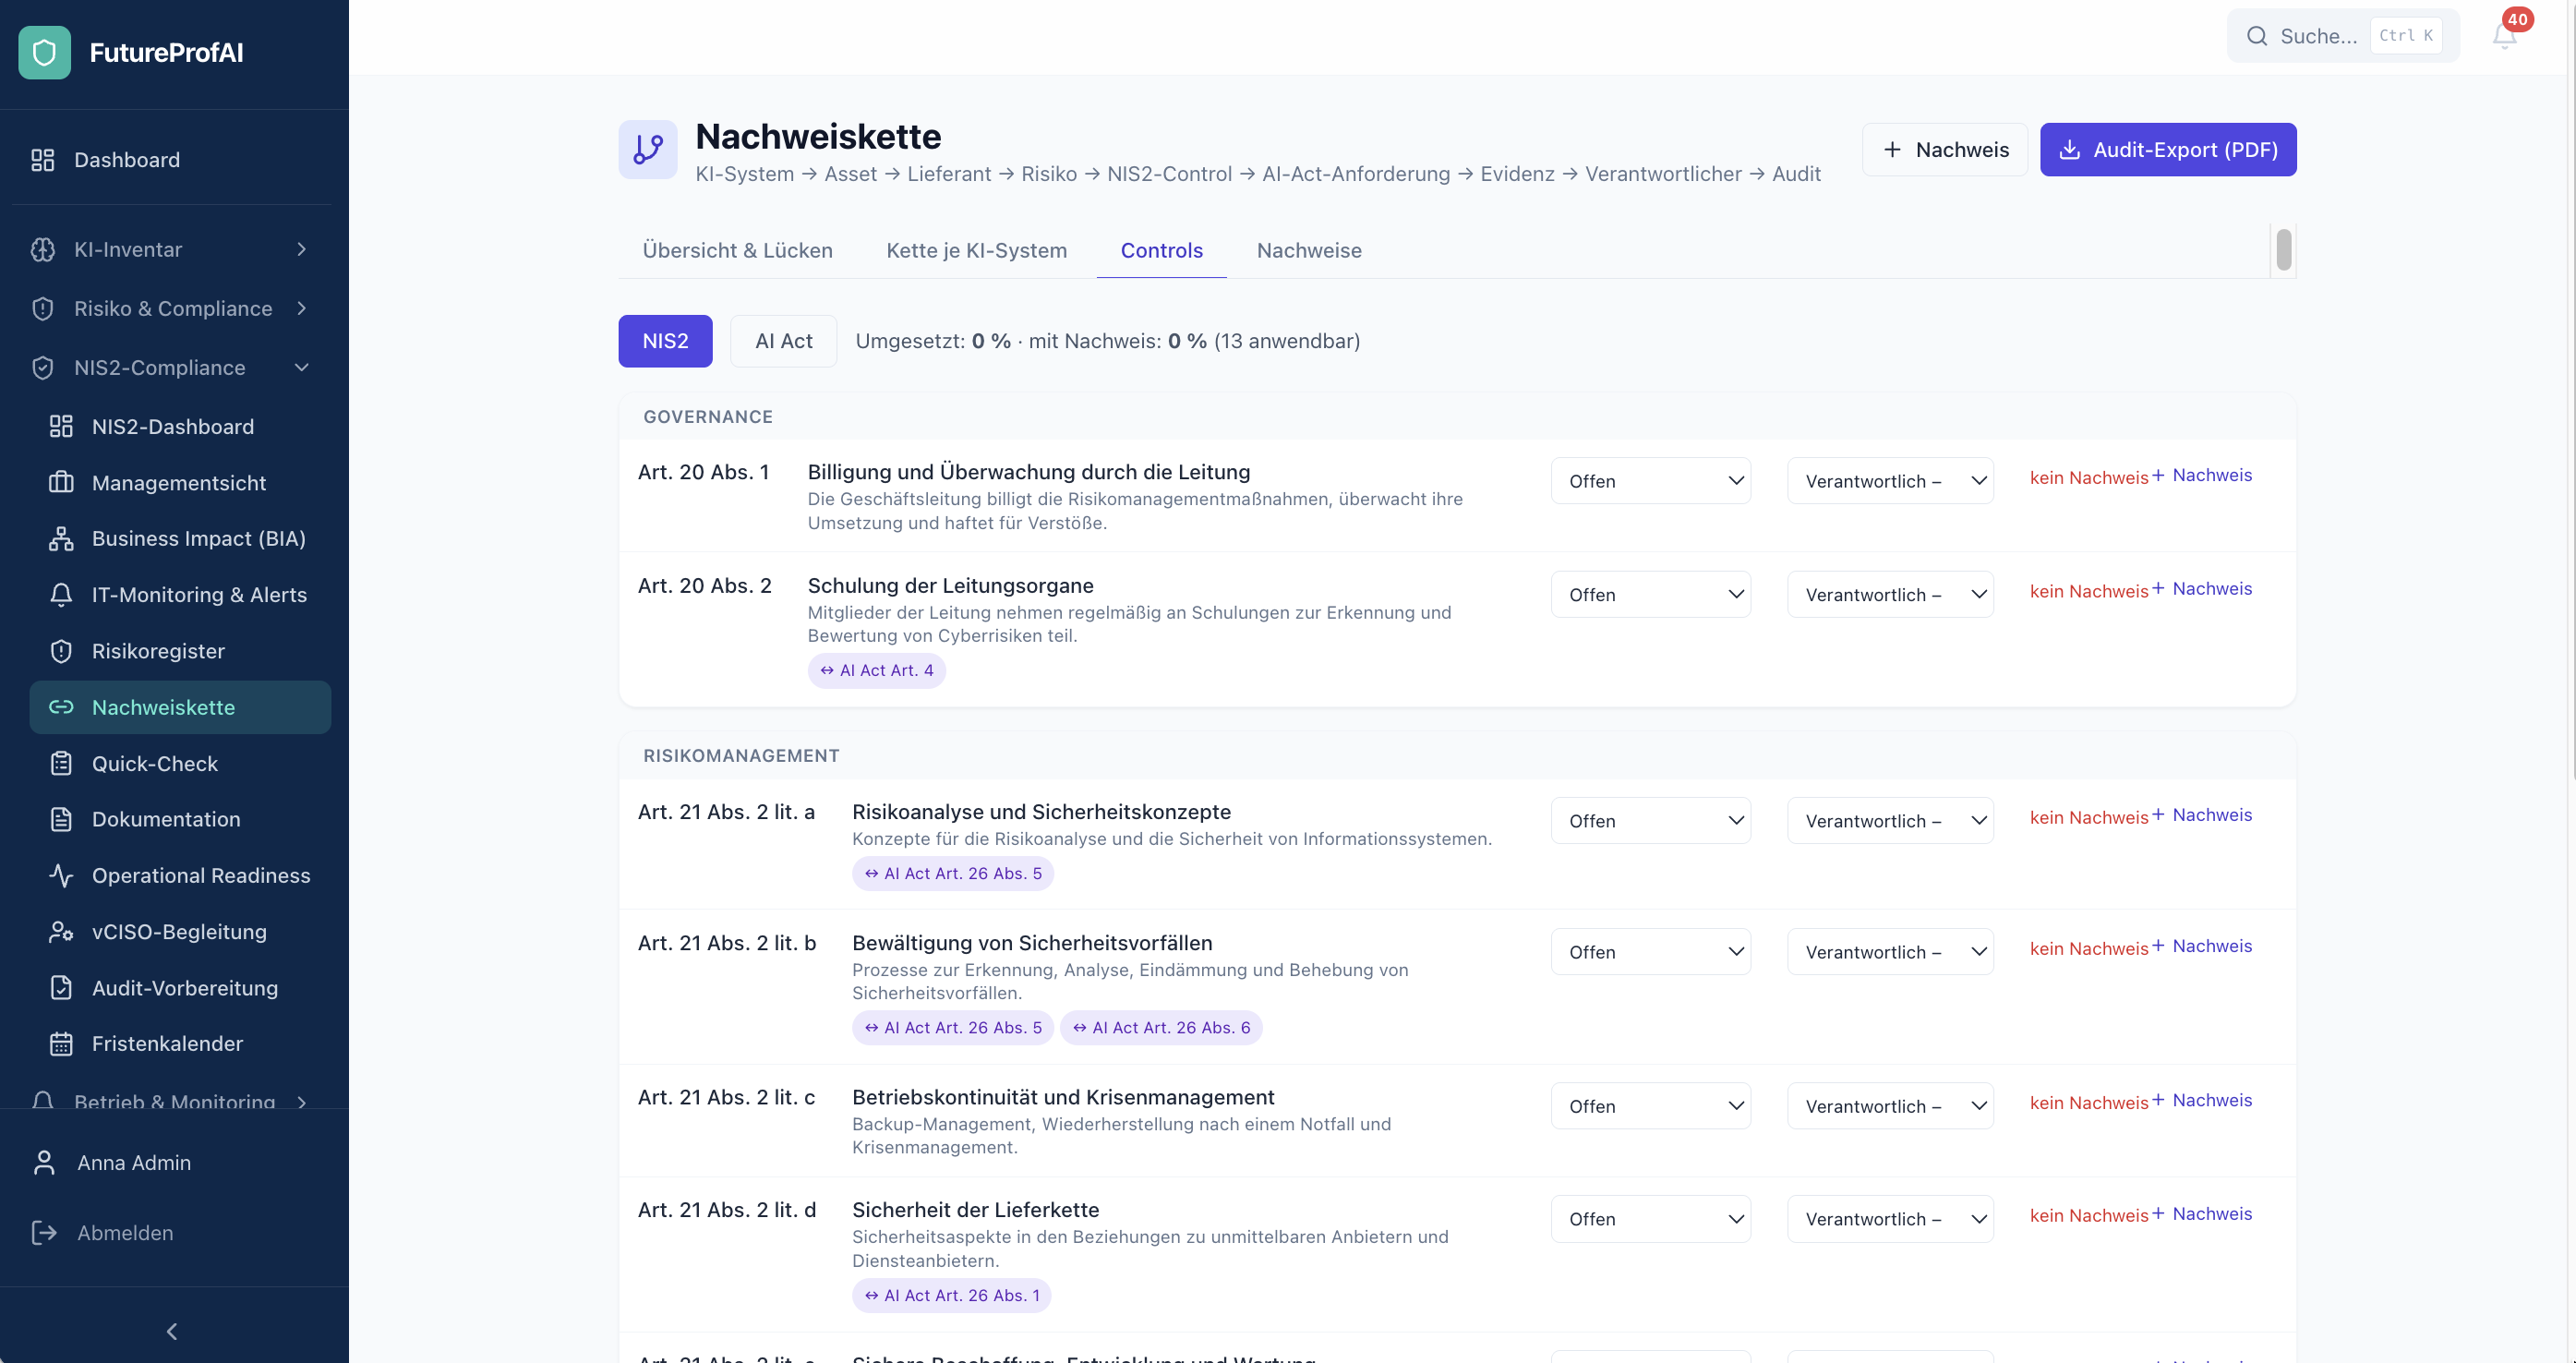
The evidence chain connects both modules in one view: you see which requirement is backed by which evidence, who is responsible – and where something is still missing.
- 1AI system
- 2IT system
- 3Supplier
- 4Risk
- 5Control
- 6Requirement
- 7Evidence
- 8Owner
Swipe sideways to explore or tap for full screen
End-to-end chain
AI systems, IT systems, suppliers, risks, controls and evidence are linked – with a separate chain for each AI system.
Gap list
Automatically shows where evidence or controls are missing.
Controls for NIS2 and the EU AI Act
With implementation status, owners and cross-references between both regulations – one piece of evidence can count for both.
Audit export as PDF
The evidence chain as a report for auditors and management.
The control catalogue is a professional working framework and does not replace legal advice.
AI governance module: all areas
Six integrated areas cover the entire AI governance lifecycle – from inventory to management reporting, aligned with the deployer obligations of the EU AI Act.
AI inventory & governance
Central recording and management of all AI systems with 30+ attributes – from lifecycle and risk categories to EU AI Act classification.
CRUD with 30+ fields, table view, filters & bulk operations
Supplier profile with GDPR/AI Act compliance & risk assessment
Technical ML documentation: performance, bias tests, limitations

Risk & compliance
Structured risk assessment, GDPR compliance checks and multi-stage approval workflows – all linked and traceable.
Categorised risk items with likelihood, impact & mitigation
Checkpoints with article mapping and status tracking
Multi-stage approval: AI Lead → Compliance → Admin

Operations & monitoring
Automated KPI monitoring with configurable thresholds, alert management and structured incident handling.
Automatic KPI monitoring with LLM action recommendations
Fingerprint-based deduplication & auto-escalation
21 predefined KPIs in 6 categories with EU AI Act reference

Reports & analysis
Compliance calendar, trend analyses and PDF reports at the touch of a button – for management and supervisory bodies.
Central cockpit for AI, risks, measures and NIS2
Dates from all modules including NIS2 reporting deadlines, colour-coded by urgency
A4 report with executive summary and all KPIs

Administration
Multi-tenancy, 7-role RBAC, audit dashboard and granular notification settings for full control.
N:M user-org mapping with JWT-based data access
15+ categories × 7 roles
Extended log with filters, timeline and CSV export

AI-powered features
AI assistants accelerate onboarding, generate risk suggestions and automatically protect personal data.
AI assistant with streaming responses & field suggestions
Automatic masking of personal data before LLM calls
Ctrl+K search across all key objects in parallel

NIS2 module: prepared when it matters
Six areas lead from the quick check through business impact, incidents and reporting deadlines to audit preparation – as the steering and evidence layer for management, IT and vCISO.
Scoping & mandatory documentation
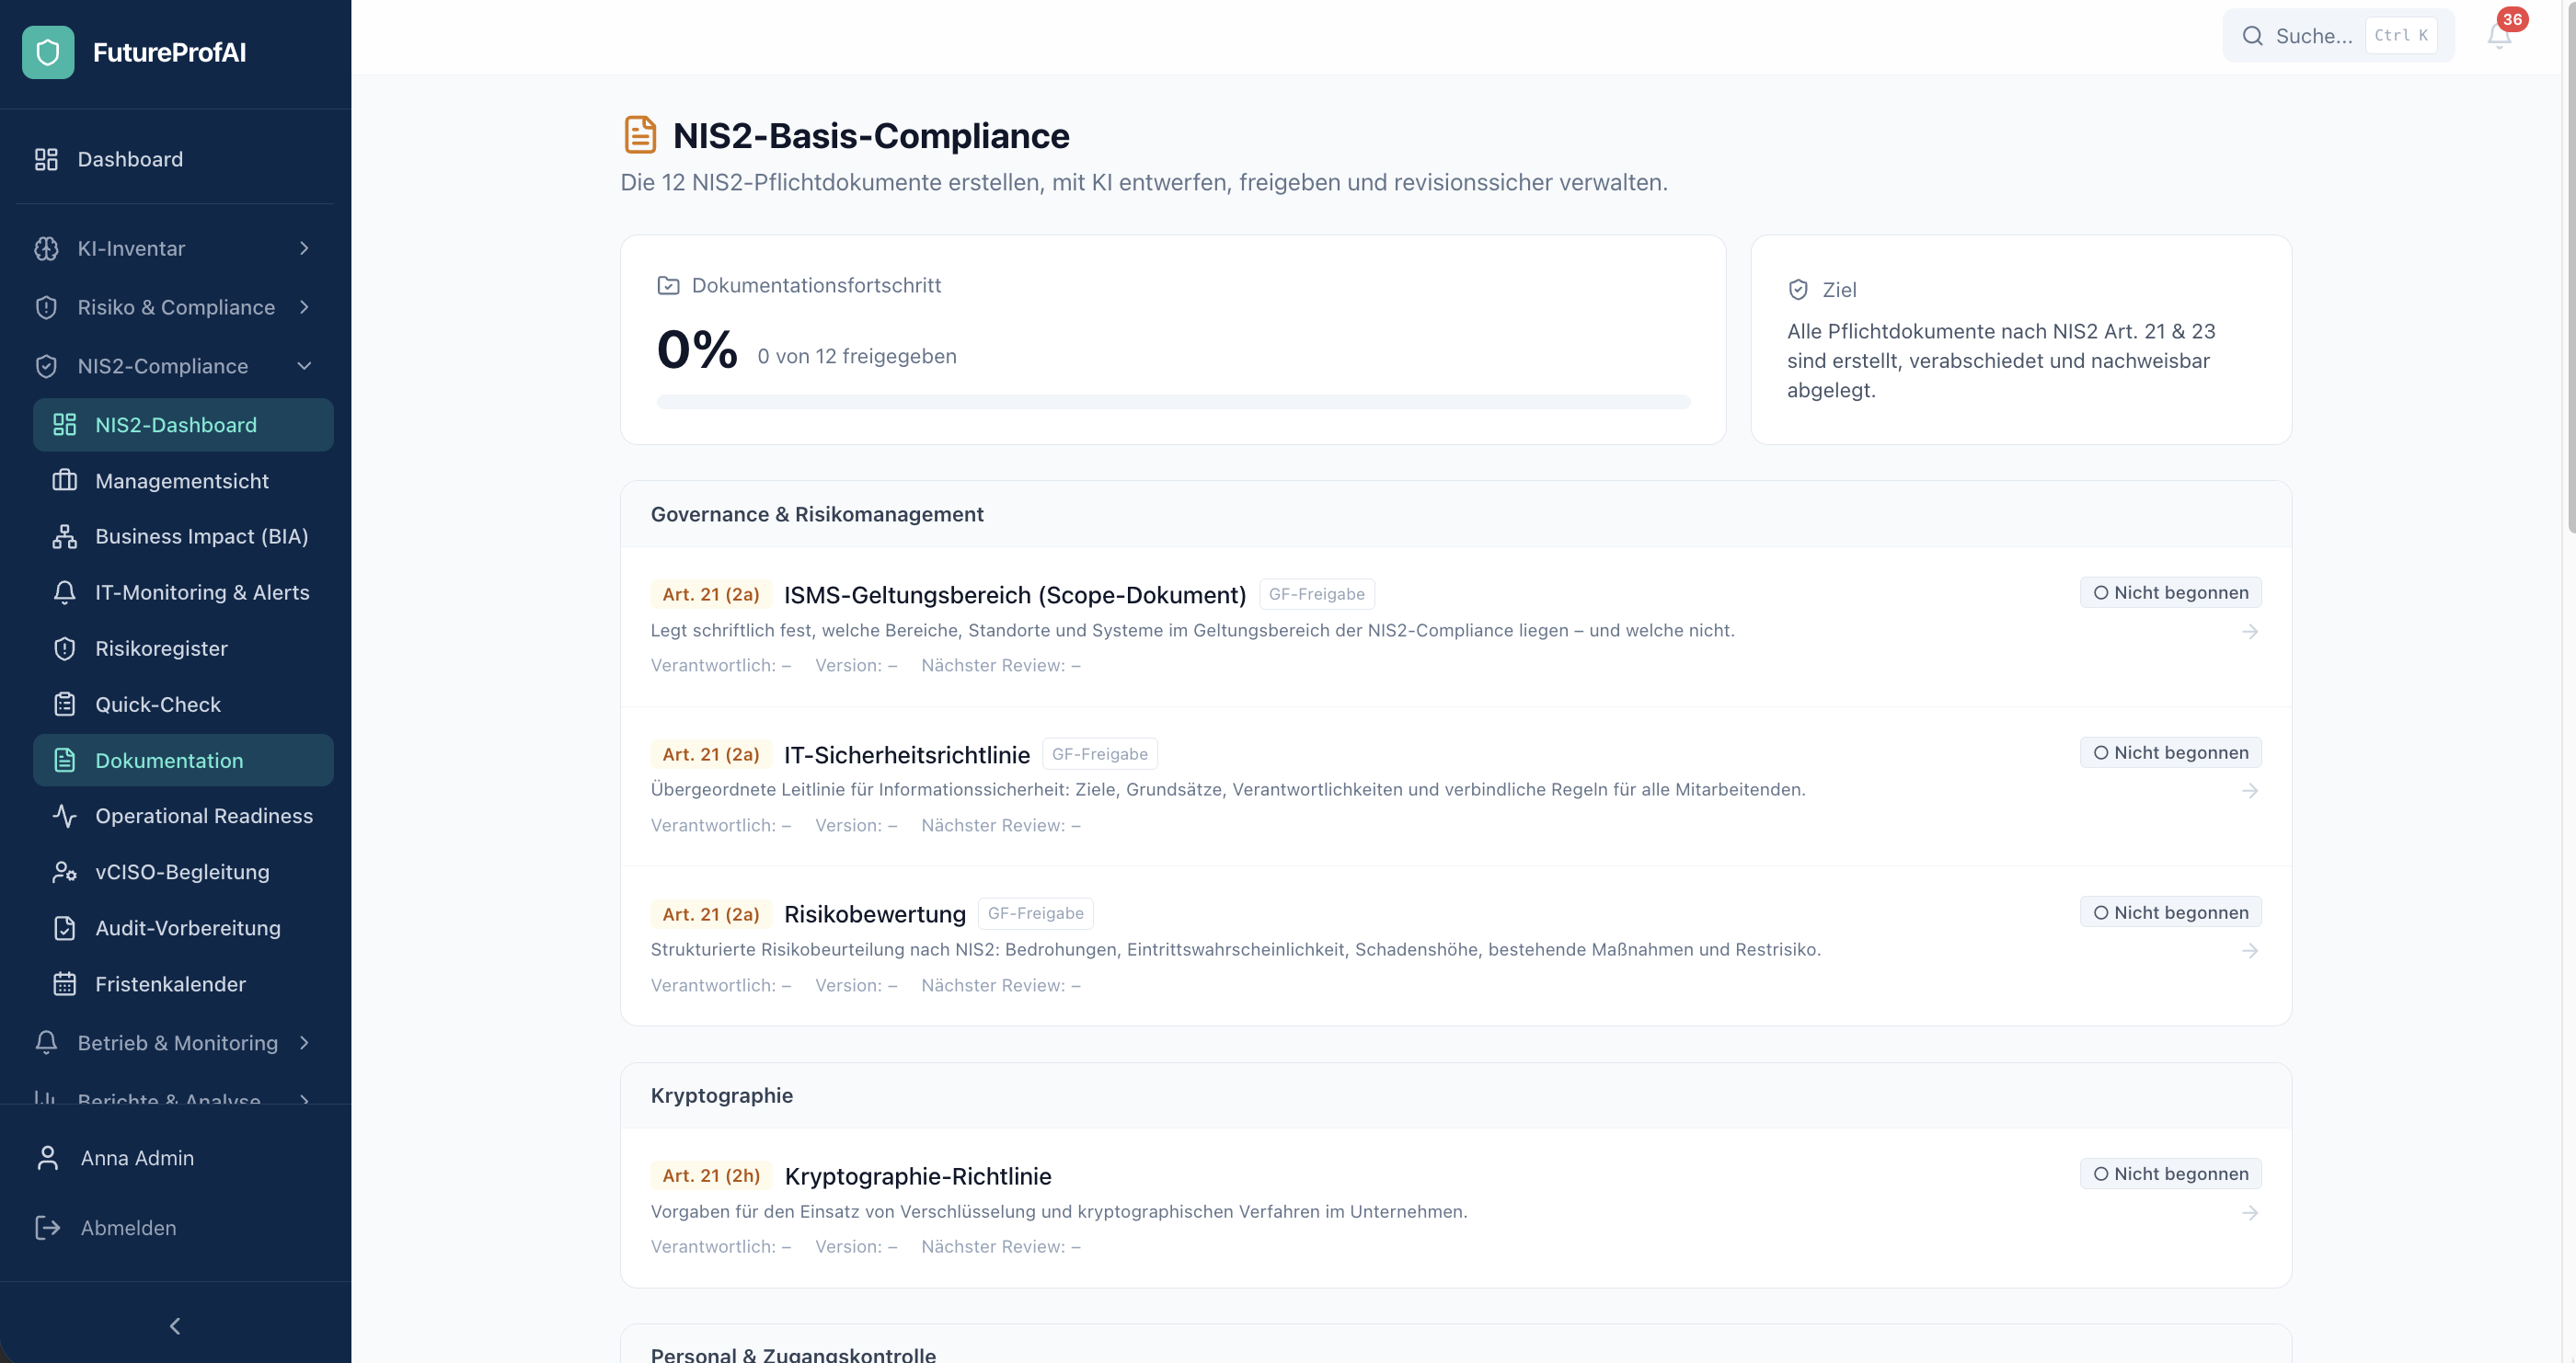
The quick check clarifies whether and how you are affected and shows the gaps. You then create the 12 mandatory documents with AI drafts and an approval workflow.
Questionnaire in 3 sections with sector selection and classification as essential or important entity
11 obligations under Art. 21 and 23 with status, priority and effort; roadmap in 3 phases
Catalogue by category, AI draft based on your company data and the quick check
Business impact, risks & supply chain
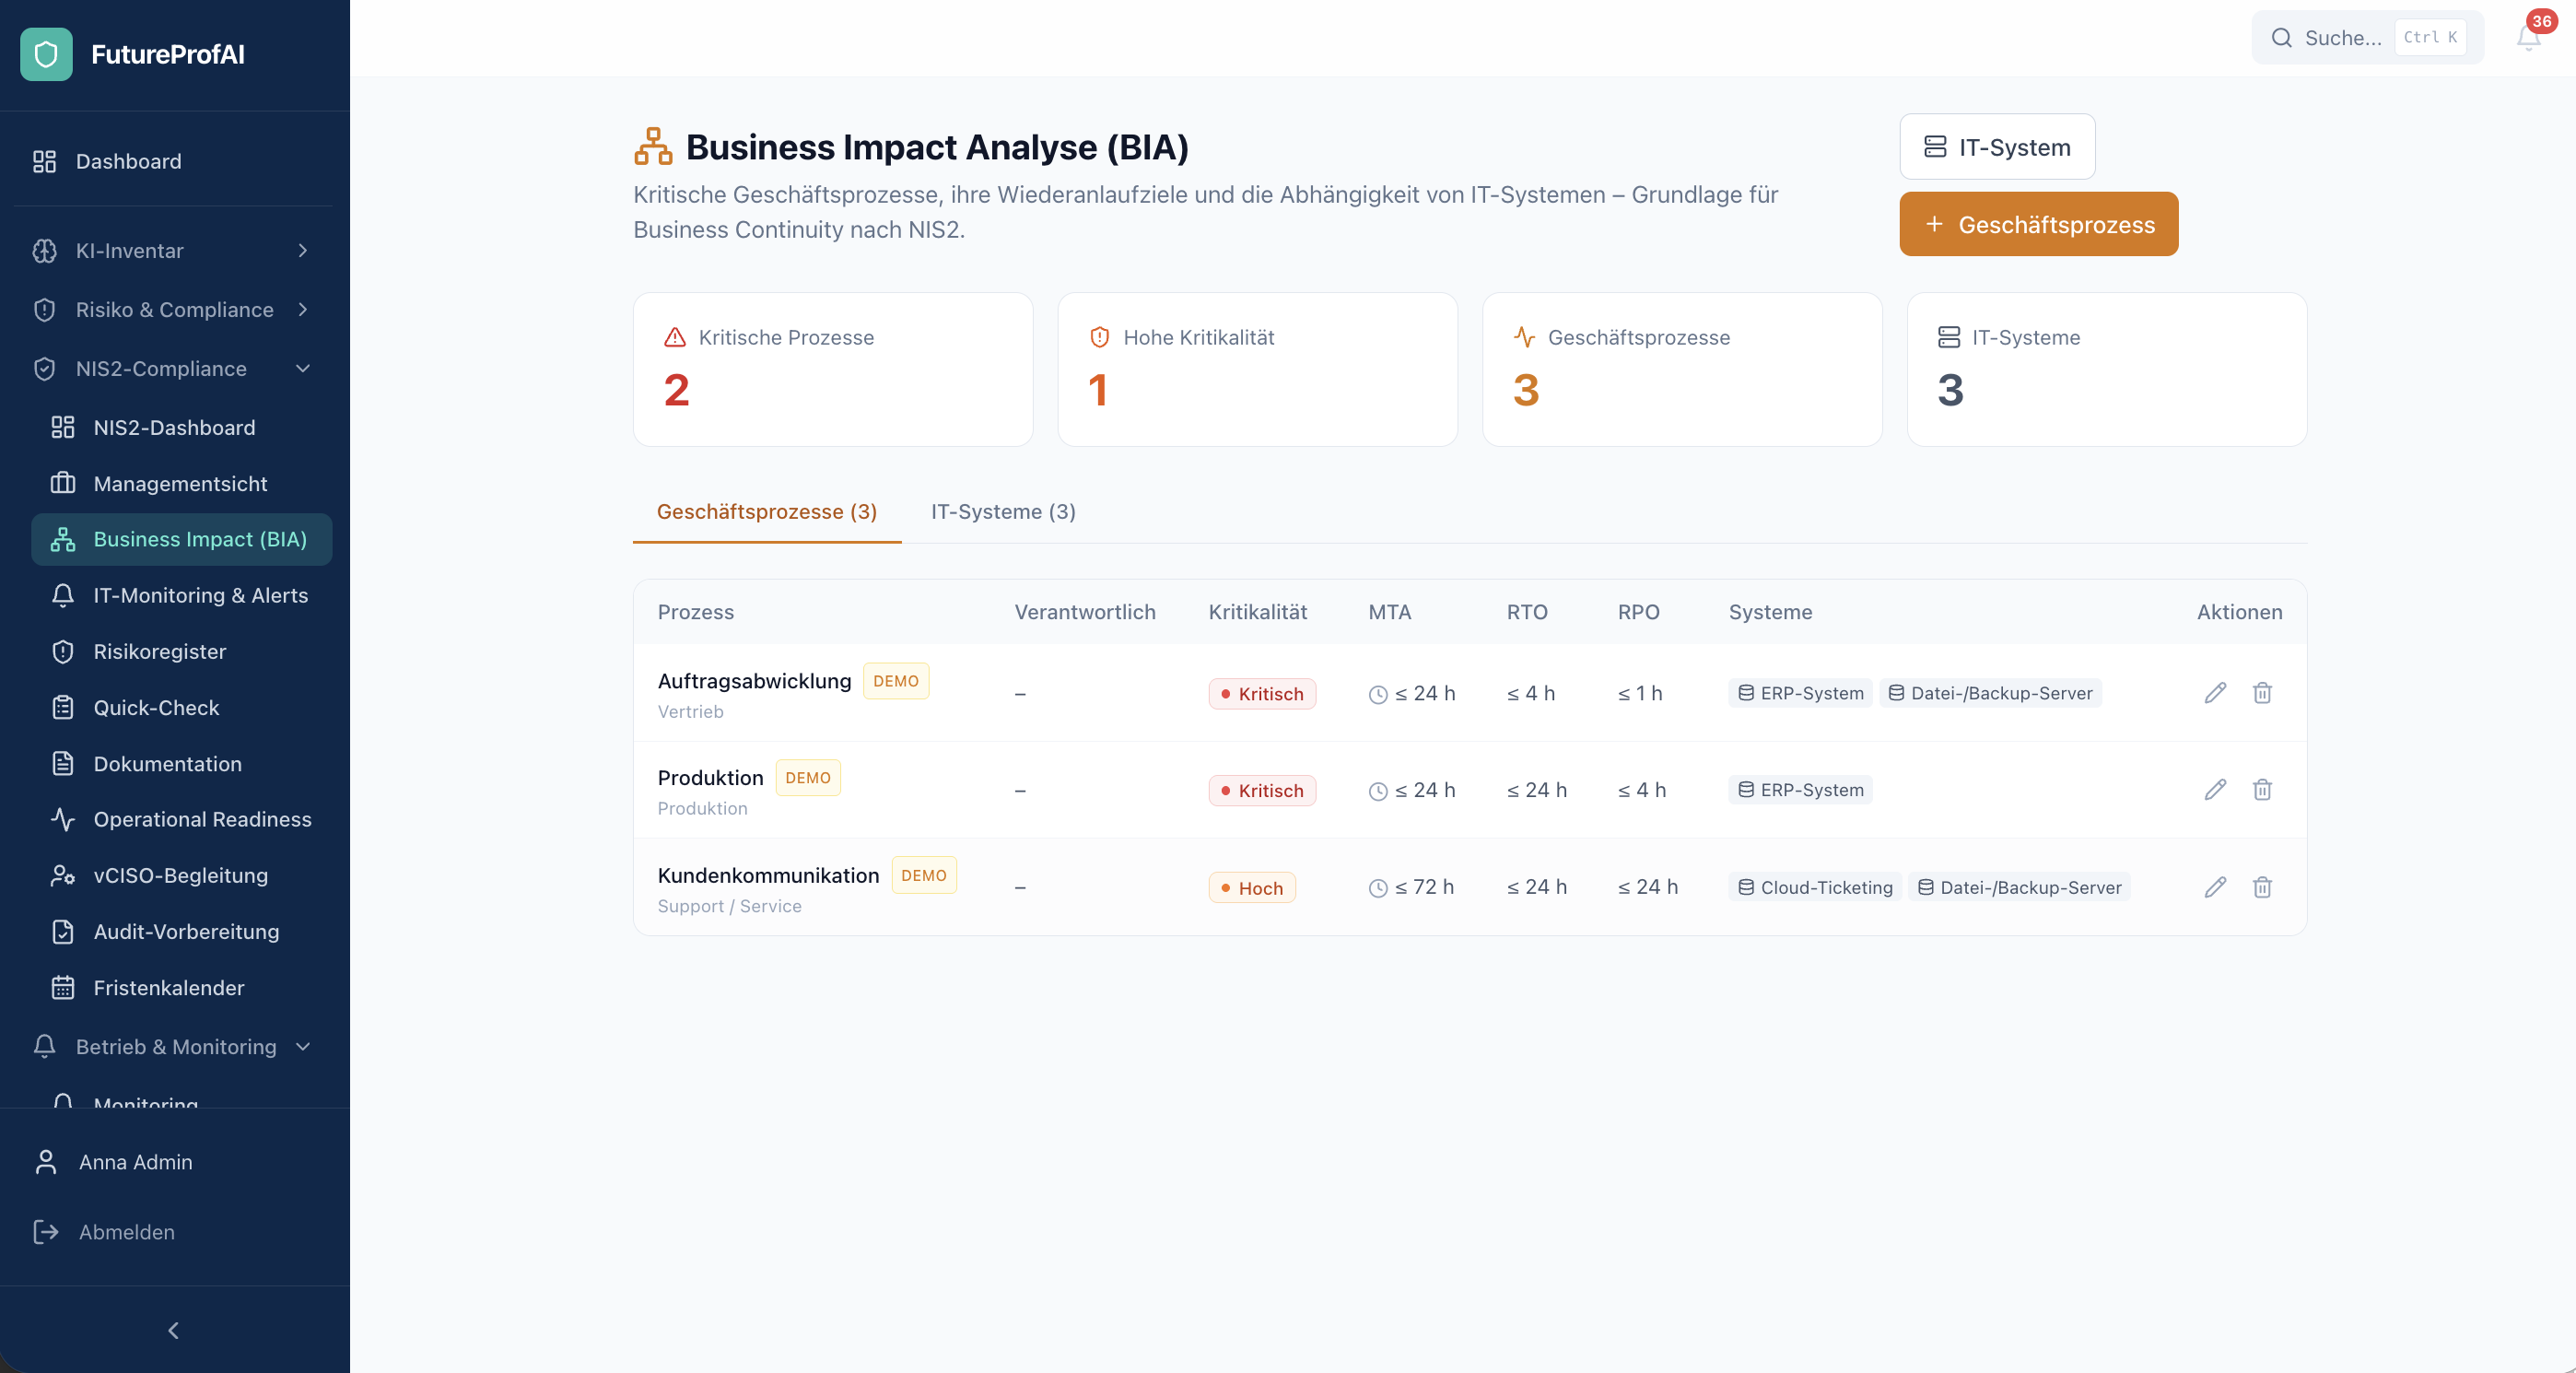
Critical business processes, their recovery targets and their dependence on IT systems and service providers – the basis for business continuity under NIS2.
Business processes with criticality and target values MTA, RTO and RPO
Process → IT system → service provider
Gross/net assessment for processes and IT systems with treatment strategy
Detection, incidents & reporting deadlines
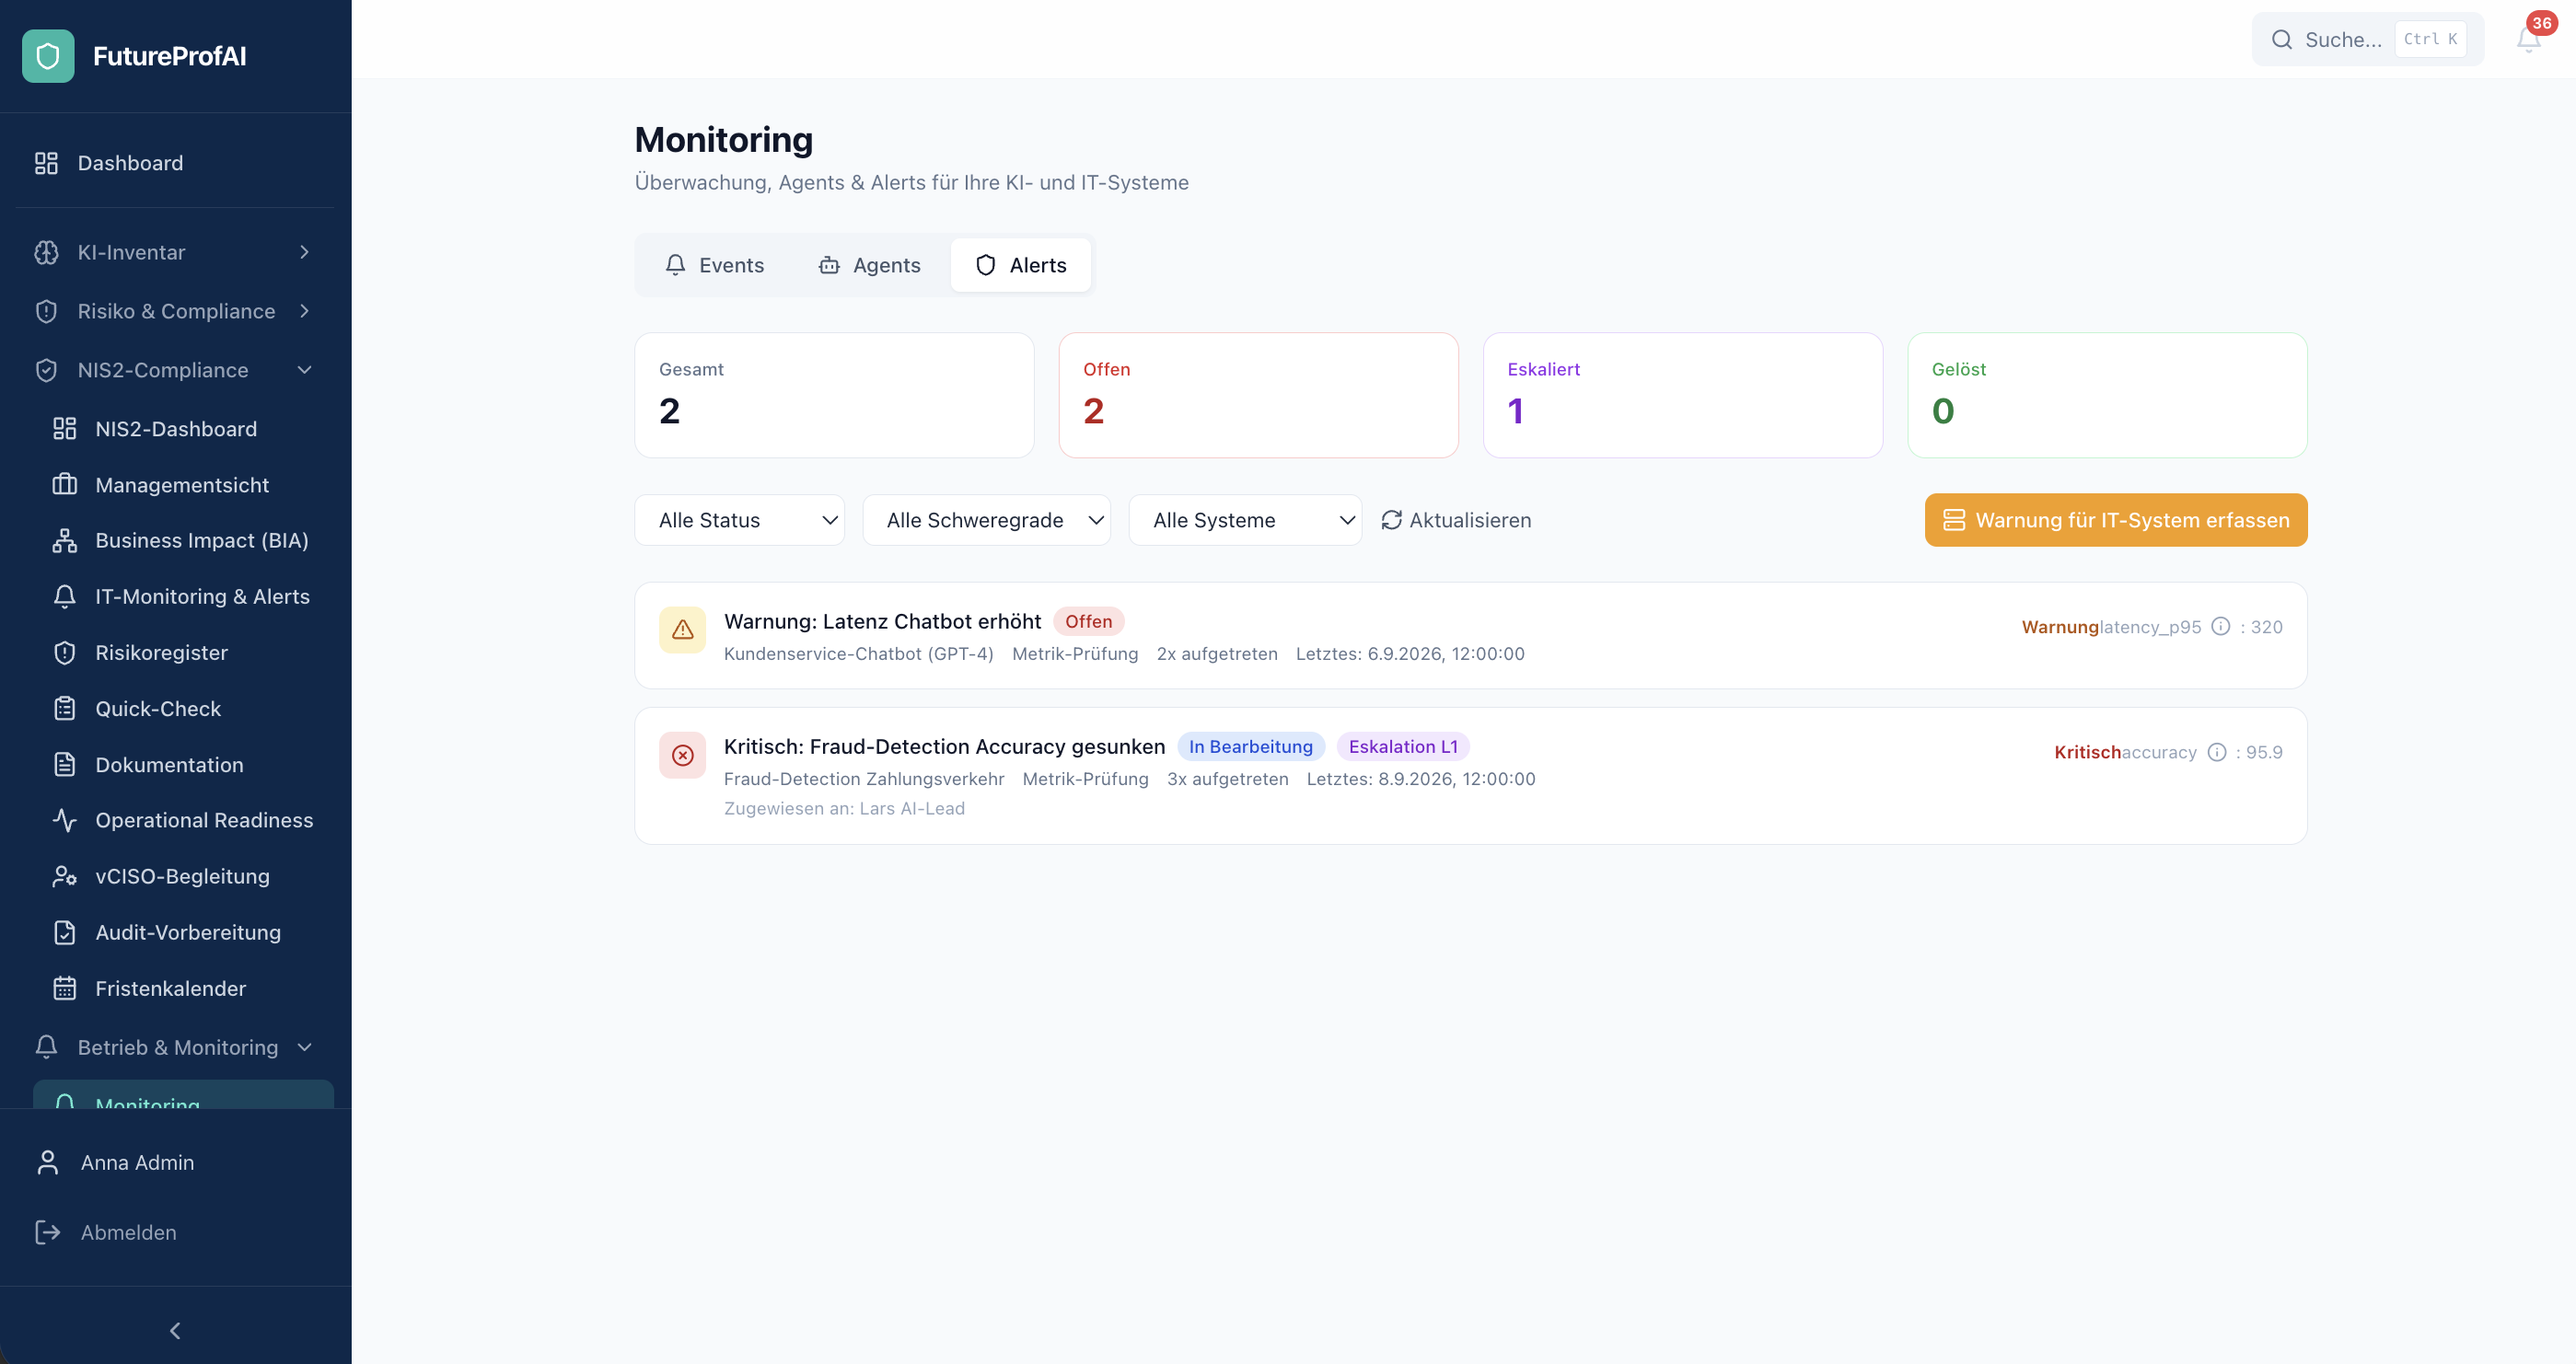
One click turns an alert into a NIS2 incident. The software checks the reporting obligation, counts down the deadlines and documents the crisis through to recovery.
Alerts on IT systems with duplicate detection and counting
Process, system and outage start are taken over from the alert
24 h early warning, 72 h notification, 1 month final report – with countdown and escalation
Operational readiness
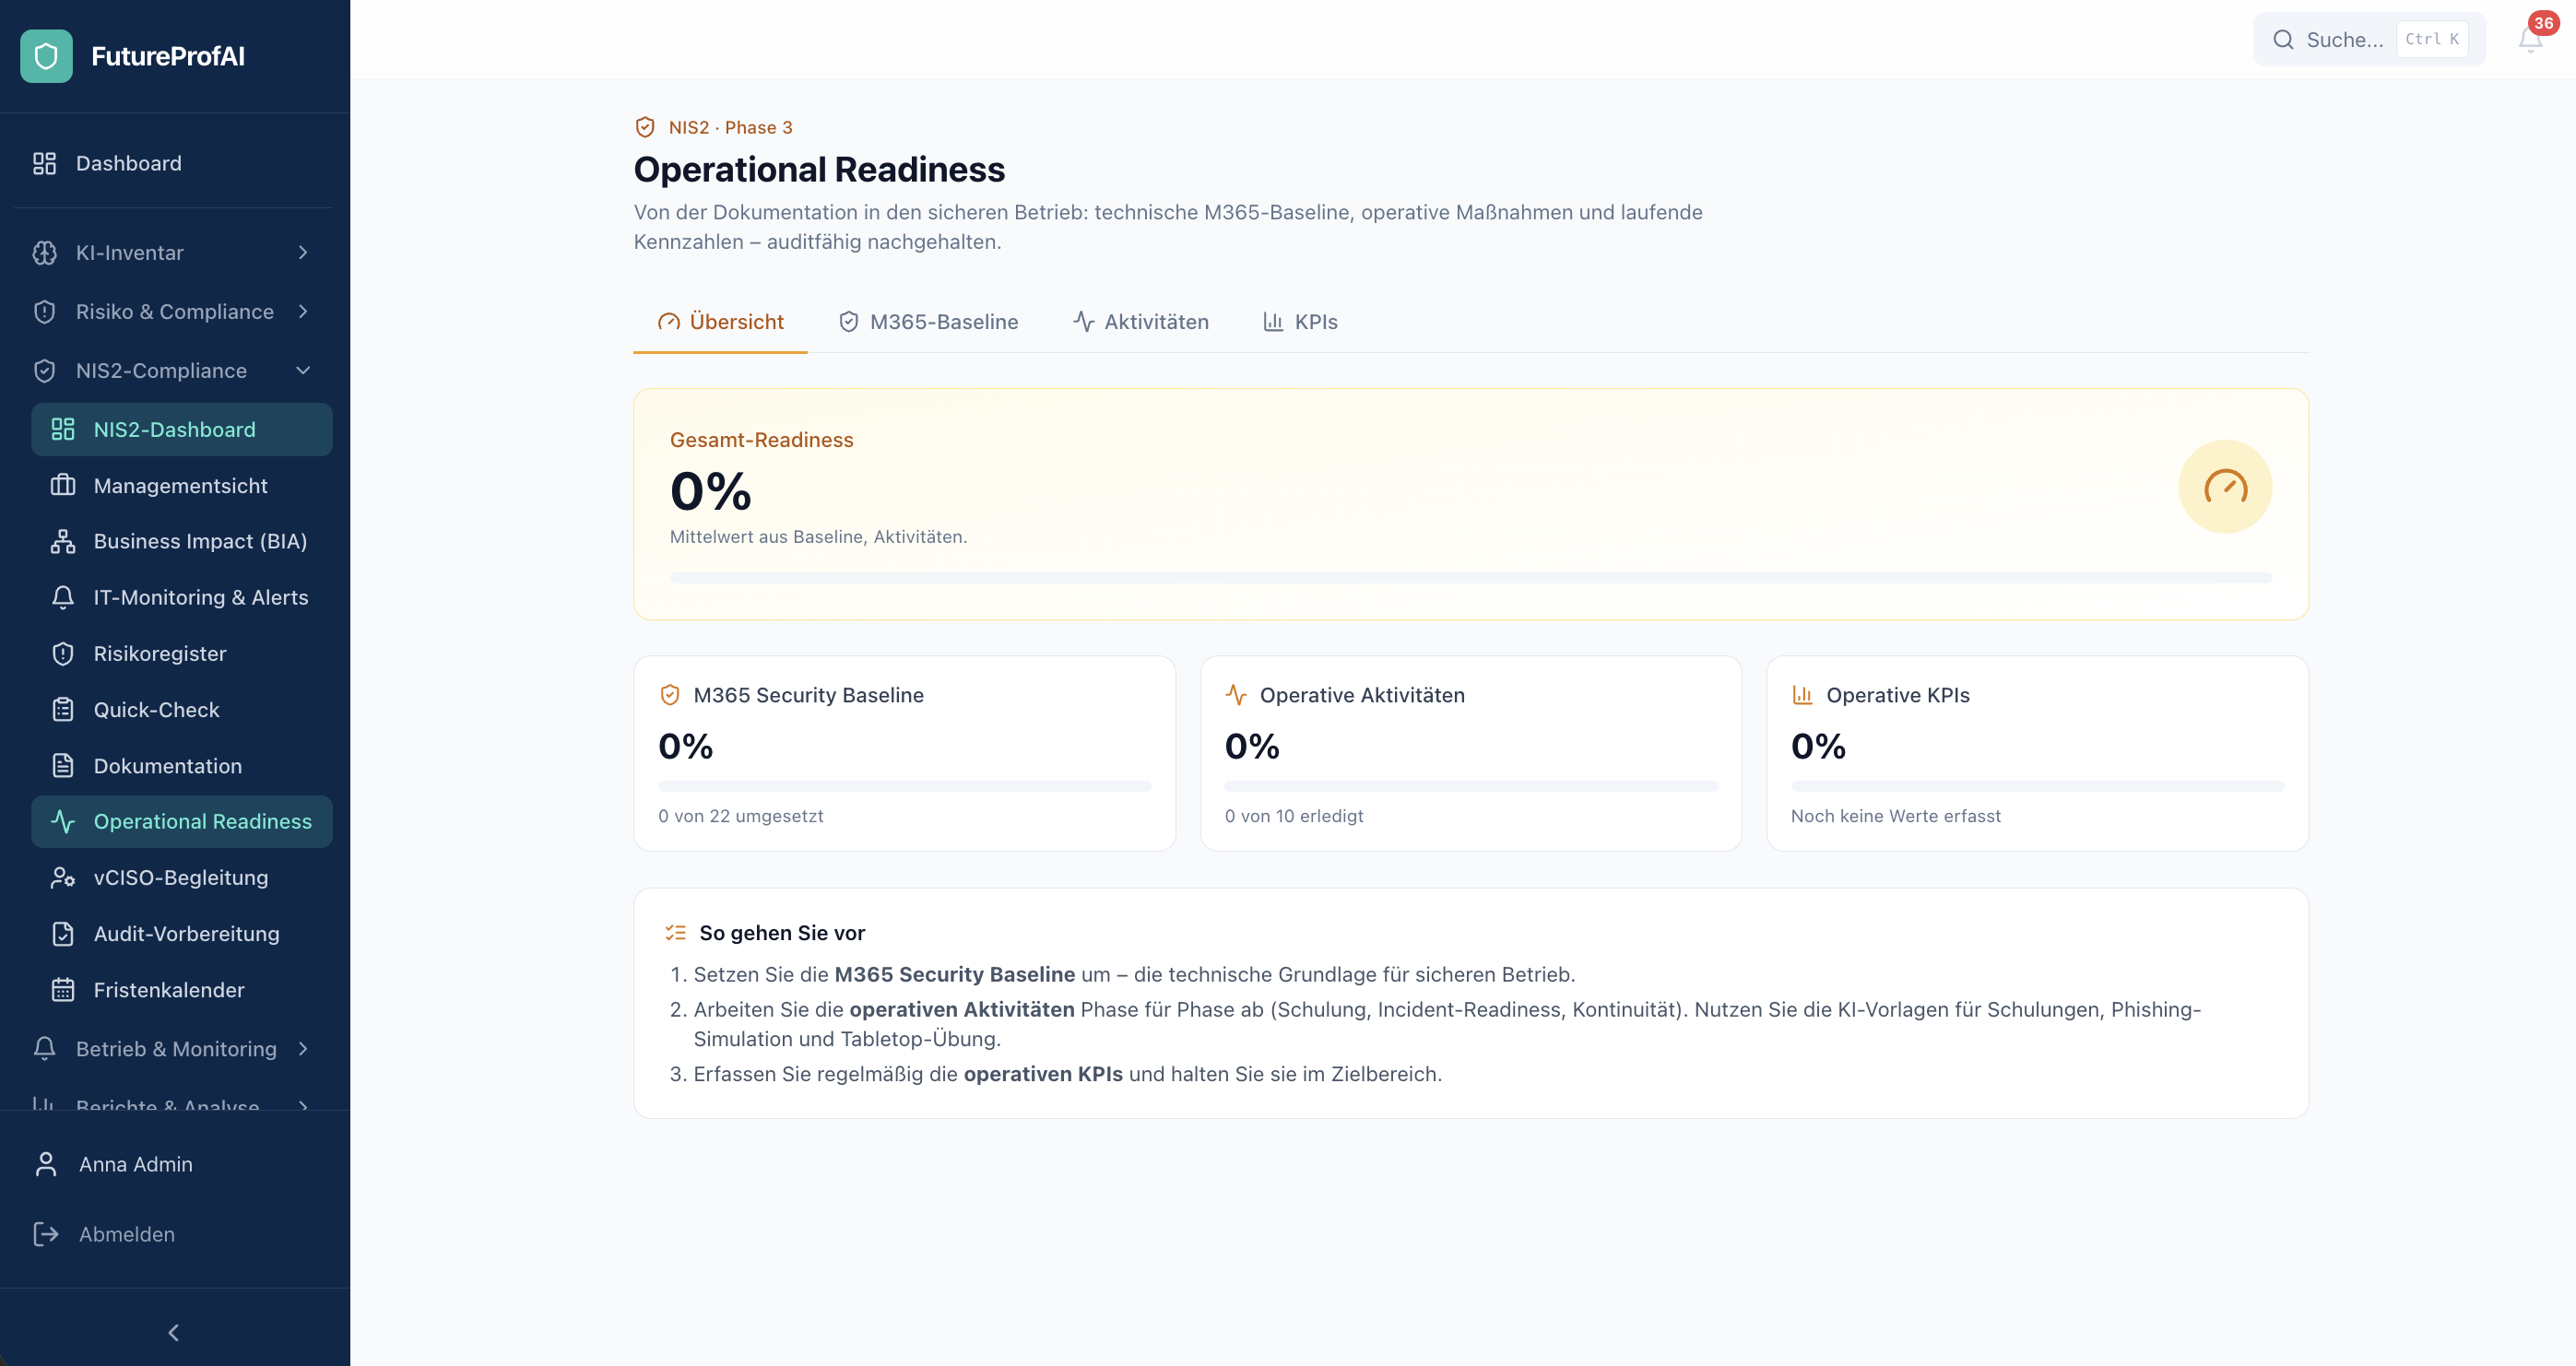
From documentation to secure operations: technical M365 baseline, operational measures and ongoing KPIs – tracked in an audit-ready way.
22 hardening items in 5 categories with status, notes and evidence
In 4 phases: technical basis, awareness, incident readiness, continuity
For training materials, phishing simulation and tabletop exercise
Management oversight & vCISO
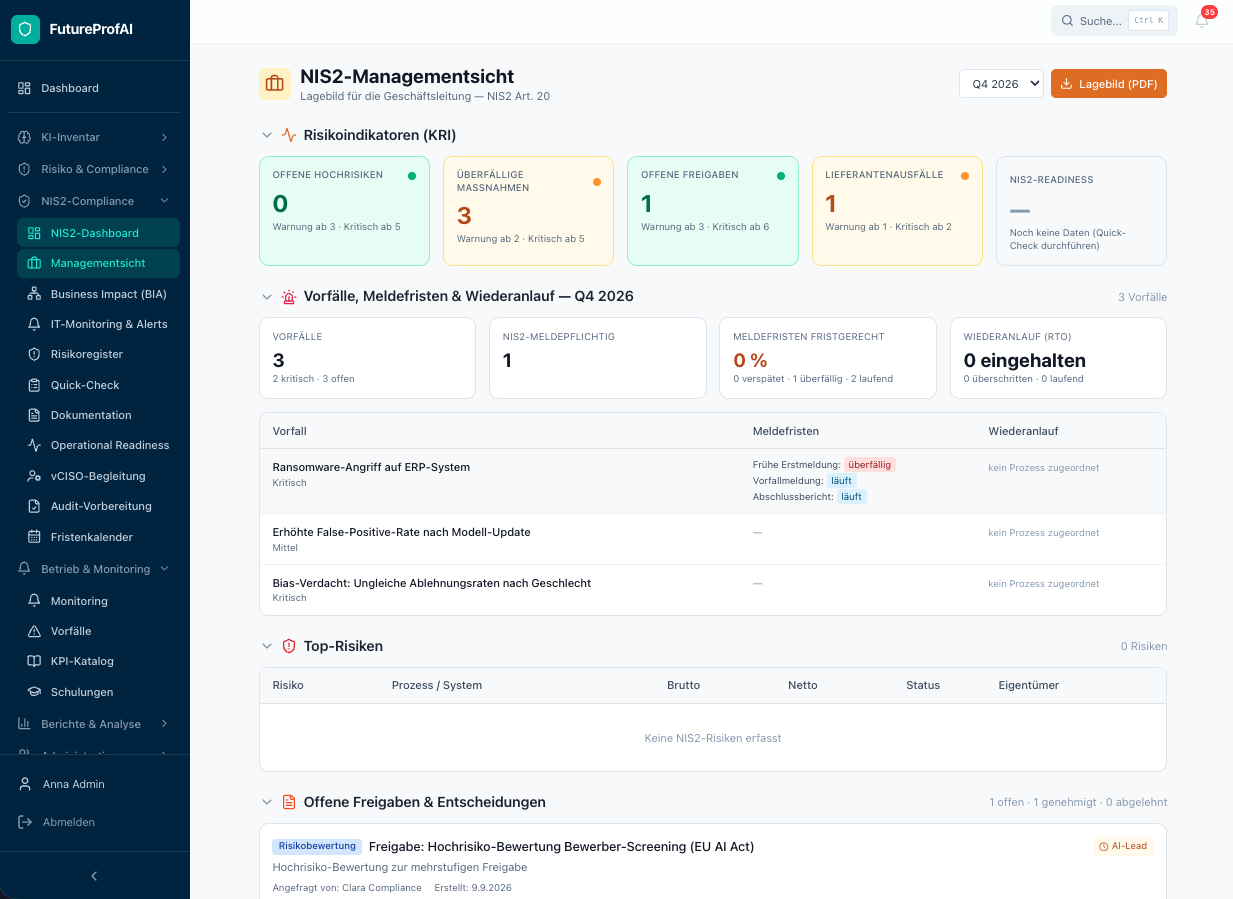
Management sees top risks, open decisions and reporting deadlines at a glance. The vCISO works with structured reviews and an annual plan.
Top risks, open decisions, KRI traffic lights and budget overview
8 sections with signature block
For regular reporting to management
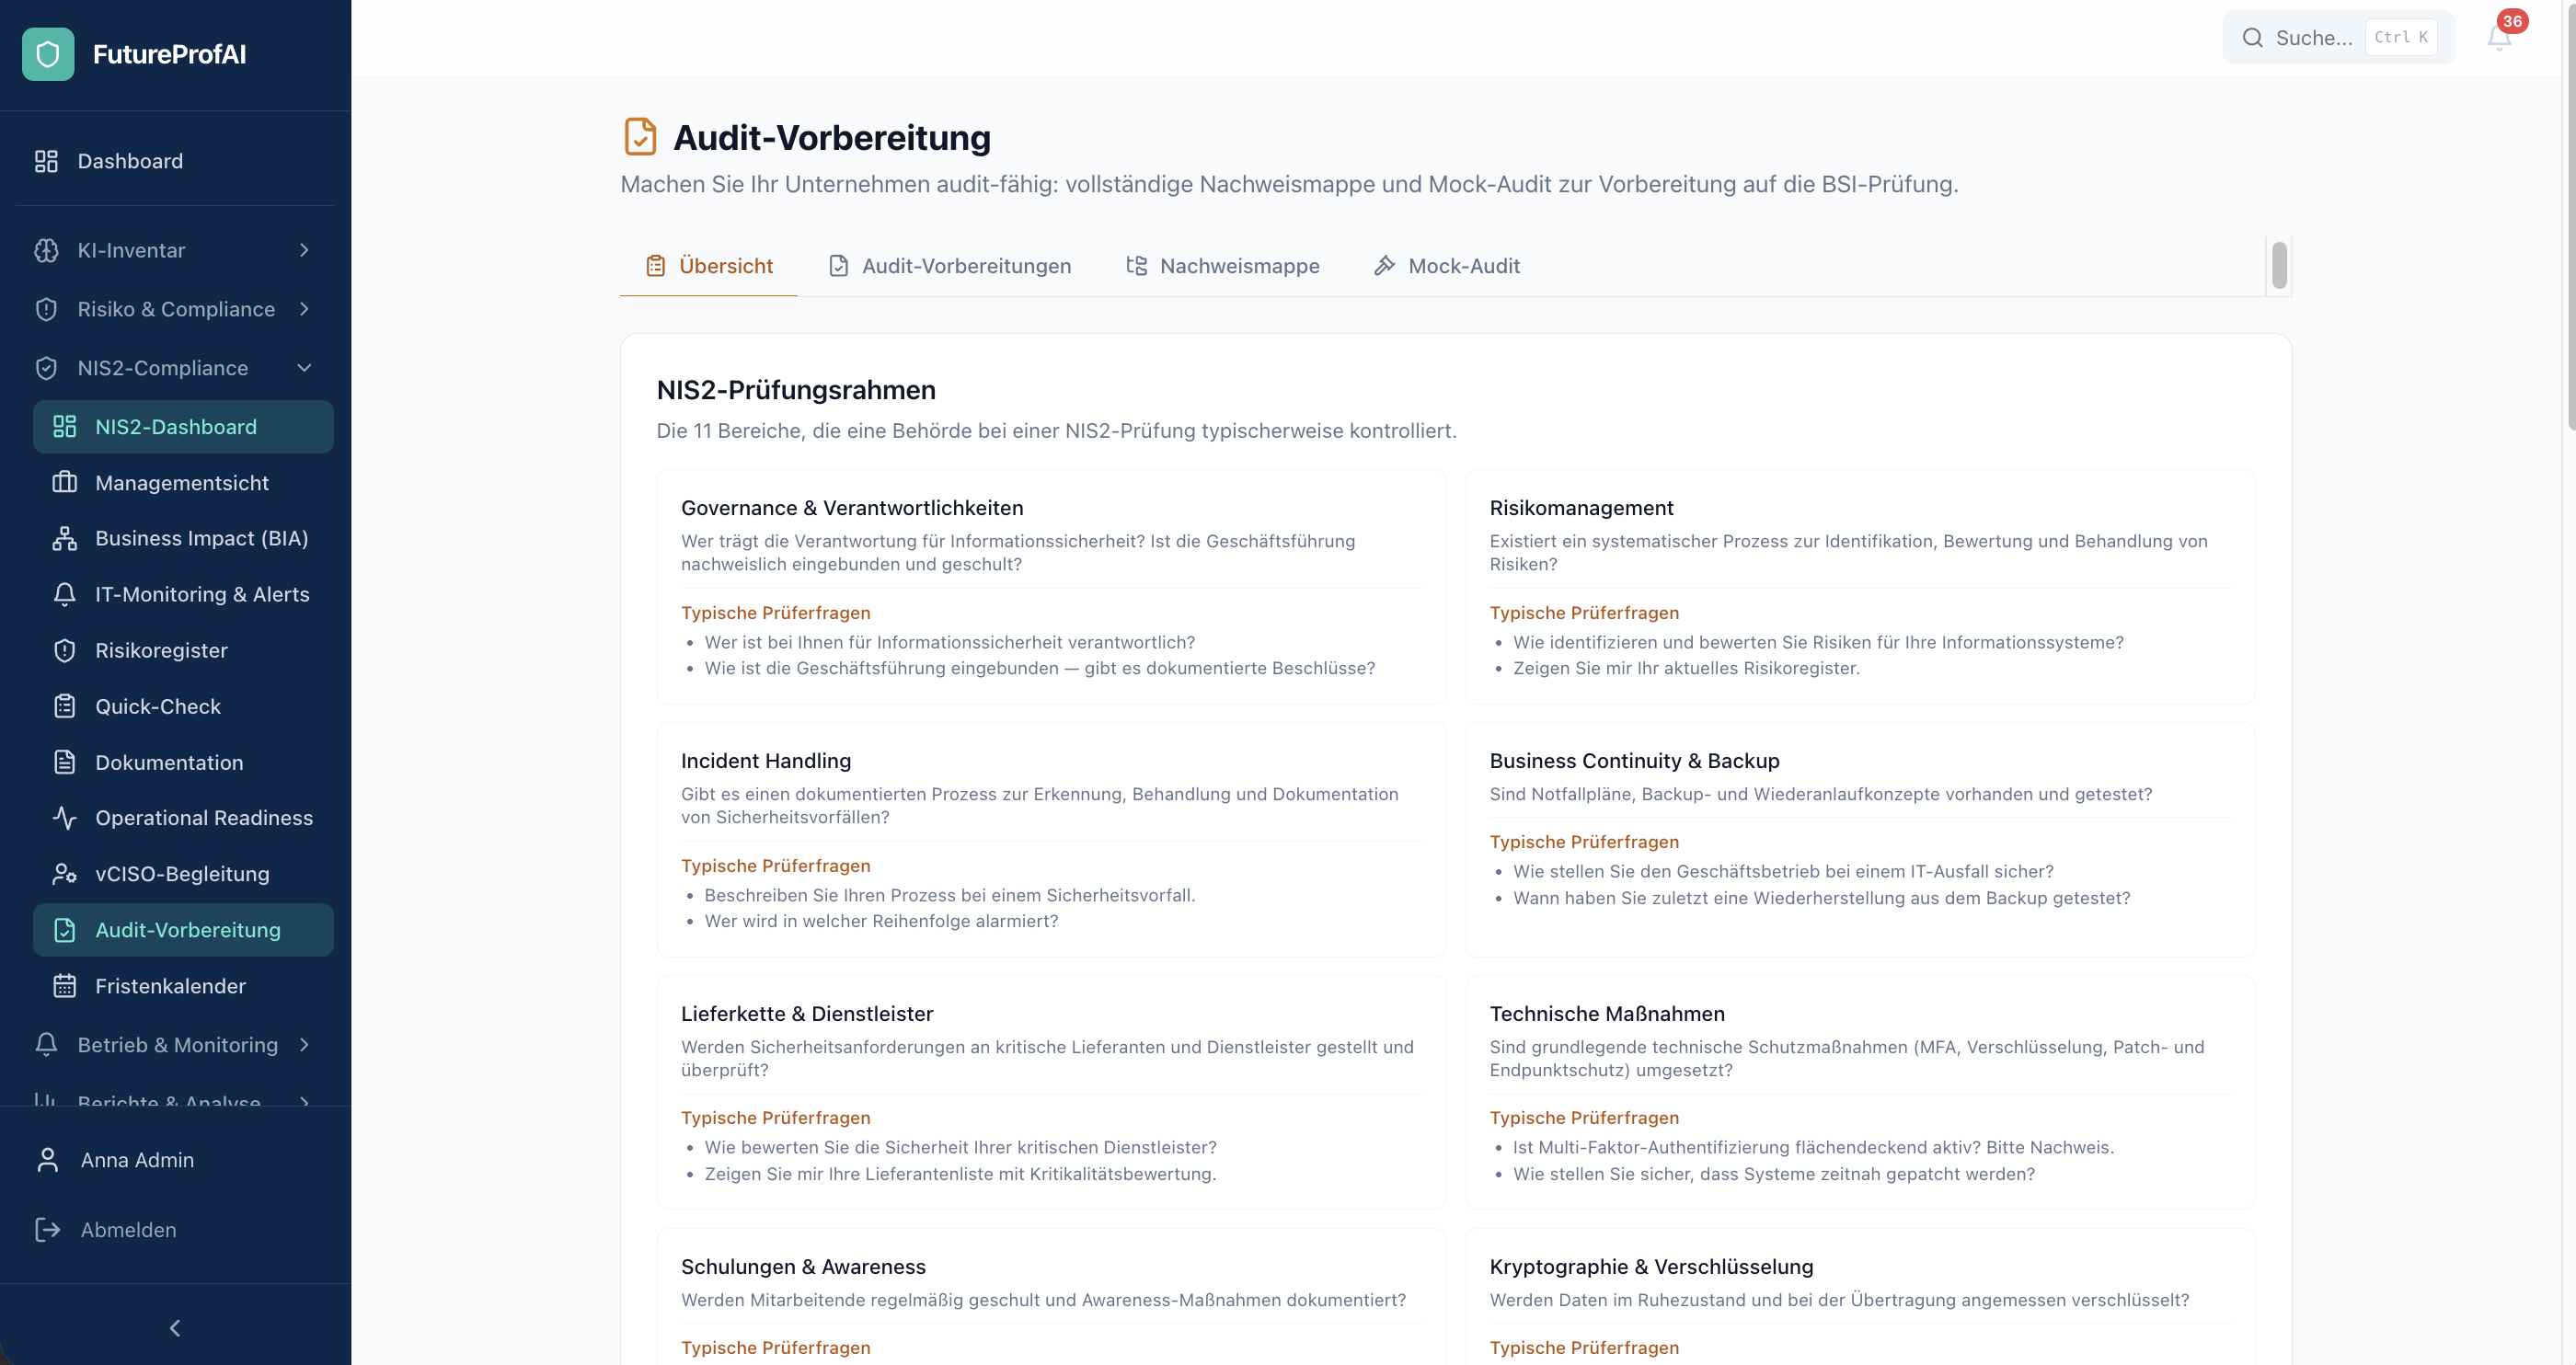
Audit preparation & evidence
A complete evidence folder and a mock audit – so you go into the audit well prepared.
With typical auditor questions and links to the NIS2 obligations
11 folders plus technical evidence, a status for each item
4 audit parts with traffic-light rating and minutes
Clearly defined: what the software deliberately does not do
FutureProfAI is the steering and evidence layer for NIS2 – not a replacement for your security technology or your legal advice. The software complements your existing tools and service providers.
- No technical attack detection (SIEM/EDR)
- No forensics
- Not the technical recovery itself
- No automatic reporting to the BSI
- No legal advice
- No certification
AI with transparency
Every AI output shows the model, reasoning and confidence – and requires human confirmation. This keeps decisions traceable and auditable.
More about NIS2AI governance and NIS2 in one software?
In 30 minutes we will show you both modules using your questions – or specifically the module you need right now.
Frequently asked questions about the software
A web software with two clearly separated modules: AI governance (six areas for the EU AI Act and ISO/IEC 42001) and NIS2 & business continuity (from scoping through incidents and reporting deadlines to audit preparation). Both modules share roles, tenants, audit log, calendar and reports and are connected through the evidence chain.
The quick check clarifies whether you are affected and shows the gaps across 11 obligations. You then create the 12 mandatory documents, analyse critical processes (business impact analysis), maintain the risk register, check the reporting obligation for incidents with the 24 h, 72 h and 1 month deadlines, and prepare for the audit with an evidence folder and a mock audit.
No. The software is the steering and evidence layer: no technical attack detection, no forensics, not the technical recovery and no automatic report to the BSI. It complements your security technology and your service providers.
You register all AI systems in a central inventory with EU AI Act classification, assess risks in a structured way, document models via model cards and control approvals through lifecycle gates G1–G5. An audit dashboard and PDF reports provide the evidence for management and auditors.
The software supports your preparation: the ISO 42001 assessment provides chapter-based scores, a gap analysis and a roadmap. A maturity assessment also measures the status per dimension. It does not replace a certification.
Before every call to a language model, the software automatically masks personal data (PII redaction). AI suggestions are shown with confidence scores so that your team can review them.
Yes. The software is multi-tenant with organisation switching and offers a role model with 7 roles and a fine-grained permission matrix with 15+ categories.
With two-factor sign-in: in addition to the password, users confirm the sign-in with a code from an authenticator app; 10 recovery codes help if a device is lost. Admins can make two-factor sign-in mandatory for all members of their organisation – in line with the NIS2 requirement for multi-factor authentication (Art. 21(2)(j)). This is complemented by roles and permissions and an audit log.
Yes. You can request free trial access or book a demo in which we show the software using your use cases.
Talk to us
Whether a quick question about the software or in-depth consulting – we are here for you.