NIS2 – prepared
when it matters
From compliance to business continuity: you know which processes are critical, keep track of every reporting deadline during an incident and can prove to management and auditors what happened. As consulting with vCISO support and as software – for mid-sized companies.
Why NIS2 now requires action
The NIS2 Implementation Act (officially: the NIS-2 Directive, transposed via the NIS2UmsuCG) has been in force since 6 December 2025 with no transition period. Around 29,500 companies in 18 sectors must now act – the BSI registration deadline already ended in March 2026. What matters now is not just documentation, but whether you can act when an incident hits.
29,500 companies affected
18 sectors – from energy and healthcare to digital trades and food production. From 50 employees or 10 million EUR turnover.
Personal liability of management
Management is personally liable for implementation. Fines of up to 10 million EUR or 2% of global annual turnover may apply.
24h reporting obligation for incidents
Early warning to the BSI within 24 hours, a full report within 72 hours, and a final report within one month.
One continuous cycle – from preparation to proof
NIS2 does not end with the last approved document. FutureProfAI supports you through every phase – before, during and after an incident.
Assess
Affected? What is missing?
Prepare
Docs, BIA, risks
Detect & report
Deadlines under control
Recover
Measurable targets
Steer & prove
Management & audit
What you achieve with FutureProfAI
Six fields of action, one software solution – each usable on its own, together a complete path from compliance to business continuity.
Applicability & obligations
Clarity in minutes
You quickly know whether and how you are affected, where the gaps are and which mandatory documents are missing – with AI drafts that your team reviews and approves.
- Classification and gap analysis across all NIS2 obligations
- Mandatory documents as AI drafts with approval workflow
- Three-phase roadmap
Business impact & dependencies
Know what is truly critical
You see how long each business process may be down and which IT systems and service providers it depends on – the foundation of any contingency planning.
- Critical processes with clear recovery targets
- Dependencies from process to system to service provider
- A supplier outage instantly shows the affected areas
Risks & measures
Nothing falls through the cracks
Risks to processes and IT systems are assessed and treated transparently. Measures have owners, deadlines and budgets – and escalate automatically when they are overdue.
- Risk assessment with documented acceptance by management
- Tiered escalation up to management
- All NIS2 deadlines in one calendar
Incidents, deadlines & crisis
Ready to act when it counts
An IT alert becomes an NIS2 incident with one click. The software checks the reporting obligation, counts down the deadlines, documents the crisis and measures recovery.
- Countdown for 24 h, 72 h and 1 month incl. GDPR check
- Crisis timeline and decision templates for management
- Recovery measured against predefined targets
Steering by management
Overview instead of gut feeling
Management sees top risks, open decisions, key figures and budget at a glance – and receives a situation report ready for signature every quarter.
- Management view with traffic lights for key risk indicators
- Quarterly situation report as PDF
- NIS2 firmly embedded in the quarterly review
Operations, audit & vCISO
Demonstrably secure
From secure operations to the audit: operational readiness with KPIs, structured audit preparation and, if desired, ongoing support from a virtual CISO.
- Operational readiness with baseline, activities and KPIs
- Mock audit, evidence folder and audit evidence per incident
- Regular reviews with vCISO support
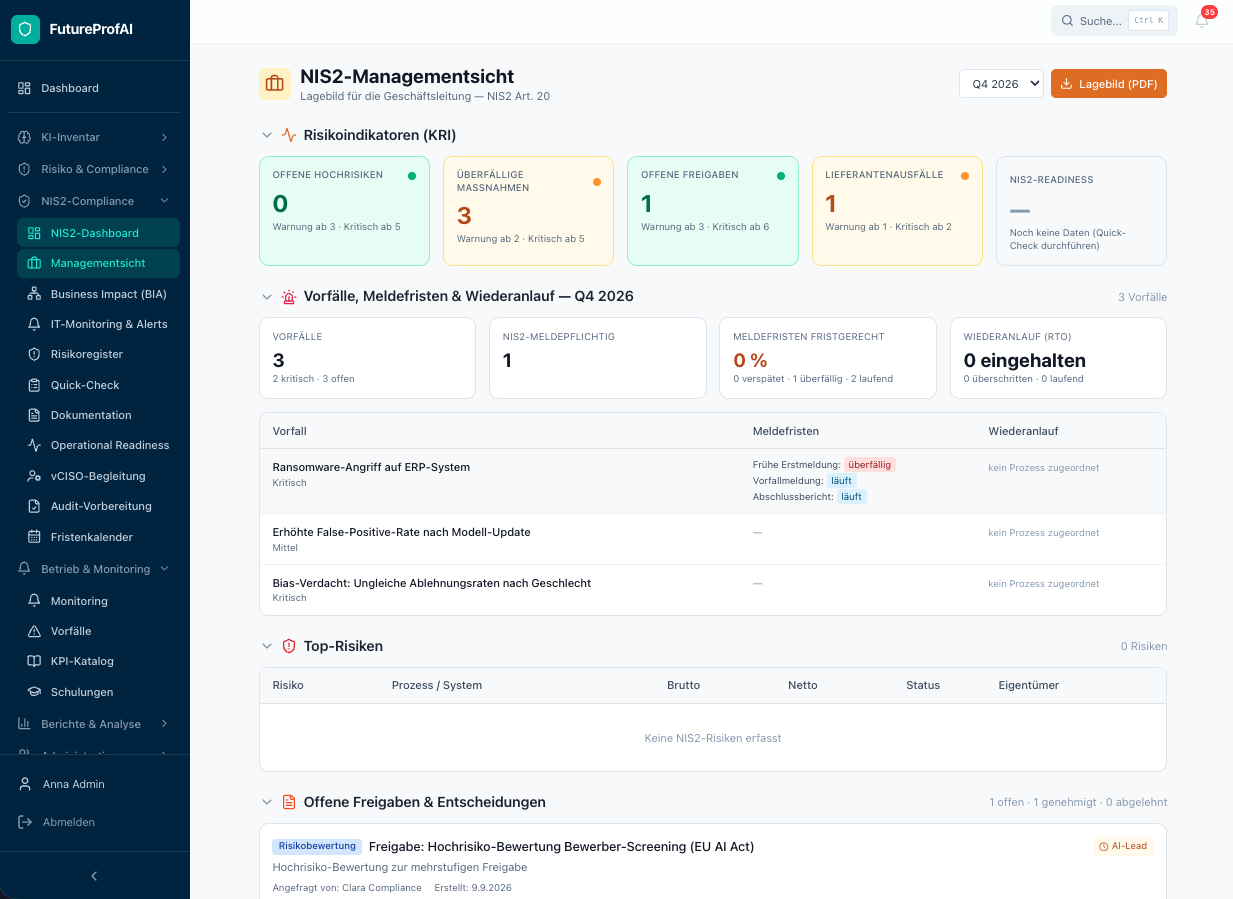
The management view: NIS2 at a glance
On a single page, management sees where the company stands – key risk indicators with traffic lights, ongoing incidents with their reporting deadlines, recovery, top risks and open decisions. The quarterly situation report can be exported directly as a PDF.
- Key risk indicators with warning and critical thresholds
- Incidents, reporting deadlines & recovery per quarter
- Open approvals and management decisions
Clearly defined: what the software deliberately does not do
FutureProfAI is the steering and evidence layer for NIS2 – not a replacement for your security technology or your legal advice. The software complements your existing tools and service providers.
- No technical attack detection (SIEM/EDR)
- No forensics
- Not the technical recovery itself
- No automatic reporting to the BSI
- No legal advice
- No certification
AI with transparency
Every AI output shows the model, reasoning and confidence – and requires human confirmation. This keeps decisions traceable and auditable.
Two paths to your NIS2 compliance
Consulting and software – strong on their own, unbeatable together.
NIS2 consulting
vCISO support at a fixed price
- Applicability & gap analysis
- Building the mandatory documentation
- Business impact analysis & contingency preparation
- Operational cybersecurity measures
- Ongoing vCISO support (retainer)
- Audit preparation & mock audit
NIS2 software
AI-assisted from compliance to crisis
- Quick check, gap analysis & mandatory documents
- Business impact analysis with dependency map
- Reporting deadline tracking with automatic warnings
- Management view & quarterly situation report
- Mock audit & audit evidence per incident
- Demo dataset: run through two crises with one click
Frequently asked questions about NIS2
Ready for when it matters?
Let us check together where you stand – free and without obligation.