Legal certainty for AI and cybersecurityin weeks, not months – at a fixed price.
For IT consultancies that need to secure their projects – and for companies that want to tackle the EU AI Act and NIS2 themselves.
- EU AI Act: most obligations from 2 Aug 2026
- NIS2: in force since 6 Dec 2025, no transition period
- Fixed-price packages – with law firms & tech partners
Compliance Maturity Check
Two topics, one point of contact
AI governance and NIS2 are different obligations – we treat them separately, with their own packages and their own software.
Two paths to legal certainty
Choose the path that fits you.
For IT consultancies & system houses
Your client asks about EU AI Act conformity – and so far you have no answer in your portfolio.
A compliance building block for your projects – under your name, with your margin.
For companies directly
Liability, fines and blocked AI projects – without robust governance.
AI inventory, risk classification, evidence and training – at a predictable fixed price.
Still unsure what the EU AI Act
means for your company?
Our quick overview explains the key requirements, risks and concrete tasks for mid-sized companies in 5 minutes.
Who does it apply to?
Every company that uses, integrates or offers AI on the market – regardless of size.
What are the risks?
Fines of up to 7% of annual turnover, liability for wrong decisions, reputational damage.
How much time is left?
The obligations take effect in stages – acting early secures competitive advantages.
Typical challenges for mid-sized companies
No AI inventory: which tools are used where?
Incomplete documentation: evidence for audits?
"Shadow AI": employees use external tools without control.
Understand the basics – then act with our governance checklist.
Does NIS2 apply to your company?
The German NIS2 implementation act has applied since 6 December 2025 – without a transition period. What matters is not only documentation, but whether you can act in an emergency.
Who is affected?
Around 29,500 companies in 18 sectors – from 50 employees or EUR 10m annual turnover.
What is at stake?
Fines of up to EUR 10m or 2% of worldwide annual turnover. Management is personally liable.
How fast must you report?
Early warning to the BSI within 24 hours, report after 72 hours, final report after one month.
Typical gaps in mid-sized companies
Unclear whether – and as which type of entity – the company is affected.
No rehearsed process for the 24-hour notification.
Management lacks a picture of risks and measures.
Our Offering
Consulting and software – for AI governance and for NIS2 alike, clearly separated.
Consulting
Fixed-price packages with experts
Productised consulting with clear packages and fixed price ranges – a separate package line for each topic.
AI Governance & EU AI Act
LAND · EXPAND · SCALE
- AI system inventory & risk triage
- Governance operating model & EU AI Act readiness
- ISO/IEC 42001 AIMS readiness
from EUR 12k
AI packagesNIS2 & Business Continuity
Quick check · Baseline · Readiness · Audit
- Applicability check & gap analysis
- Mandatory documentation & business impact analysis
- Tabletop exercise & audit preparation
from EUR 2.5k
NIS2 packagesPlus: vCISO support as a retainer from EUR 1.2k/month
Software
One software, two modules
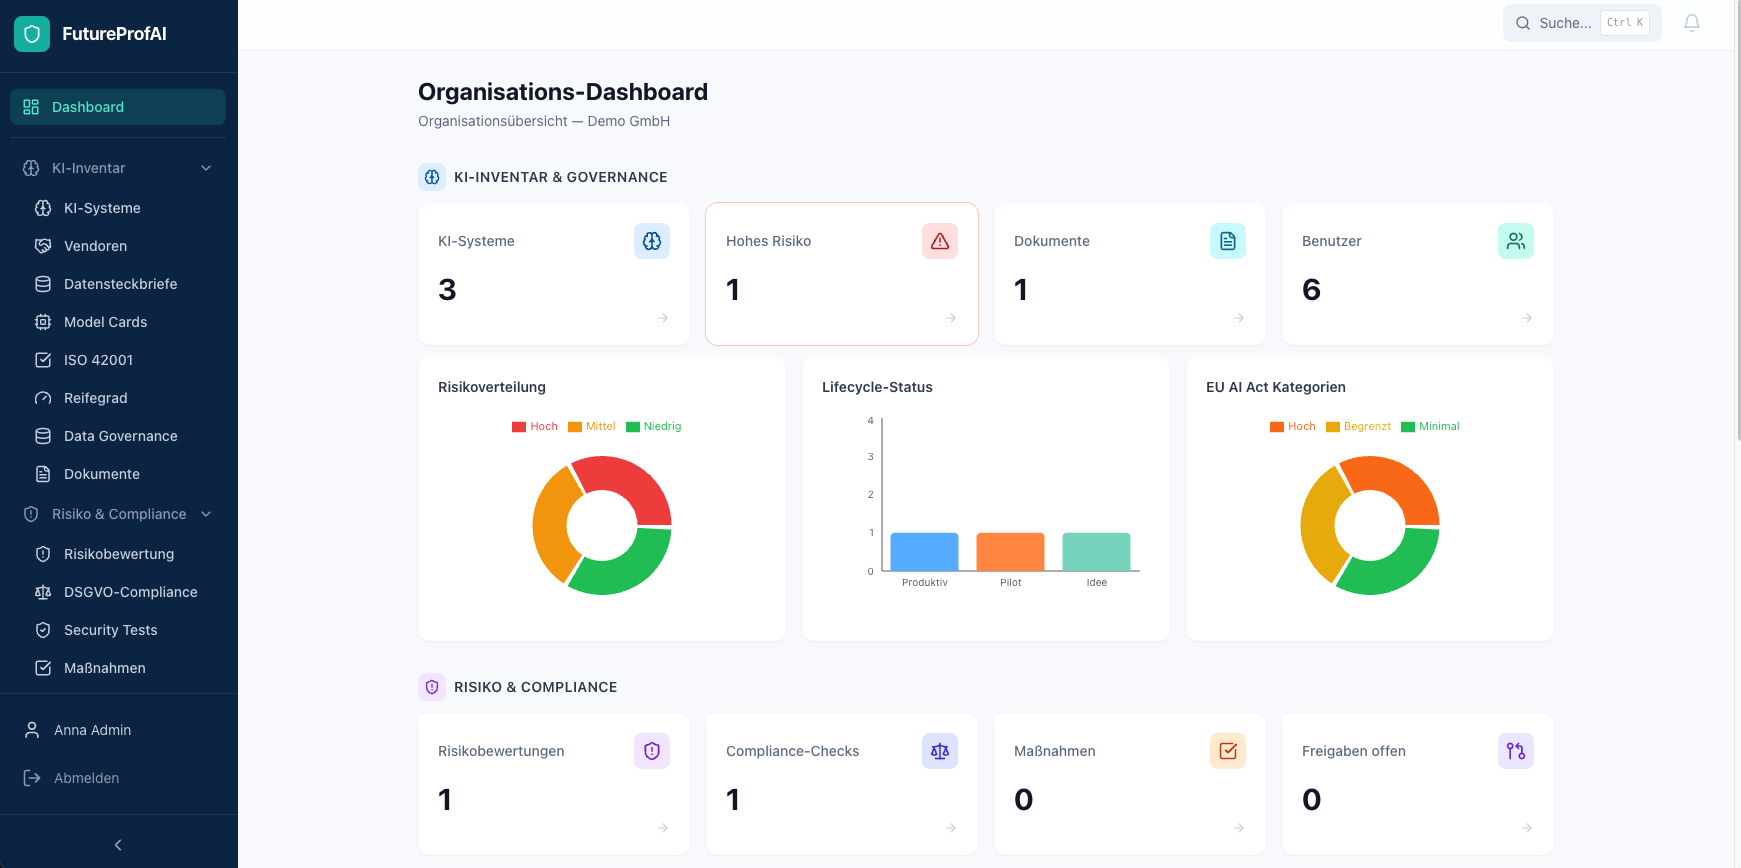
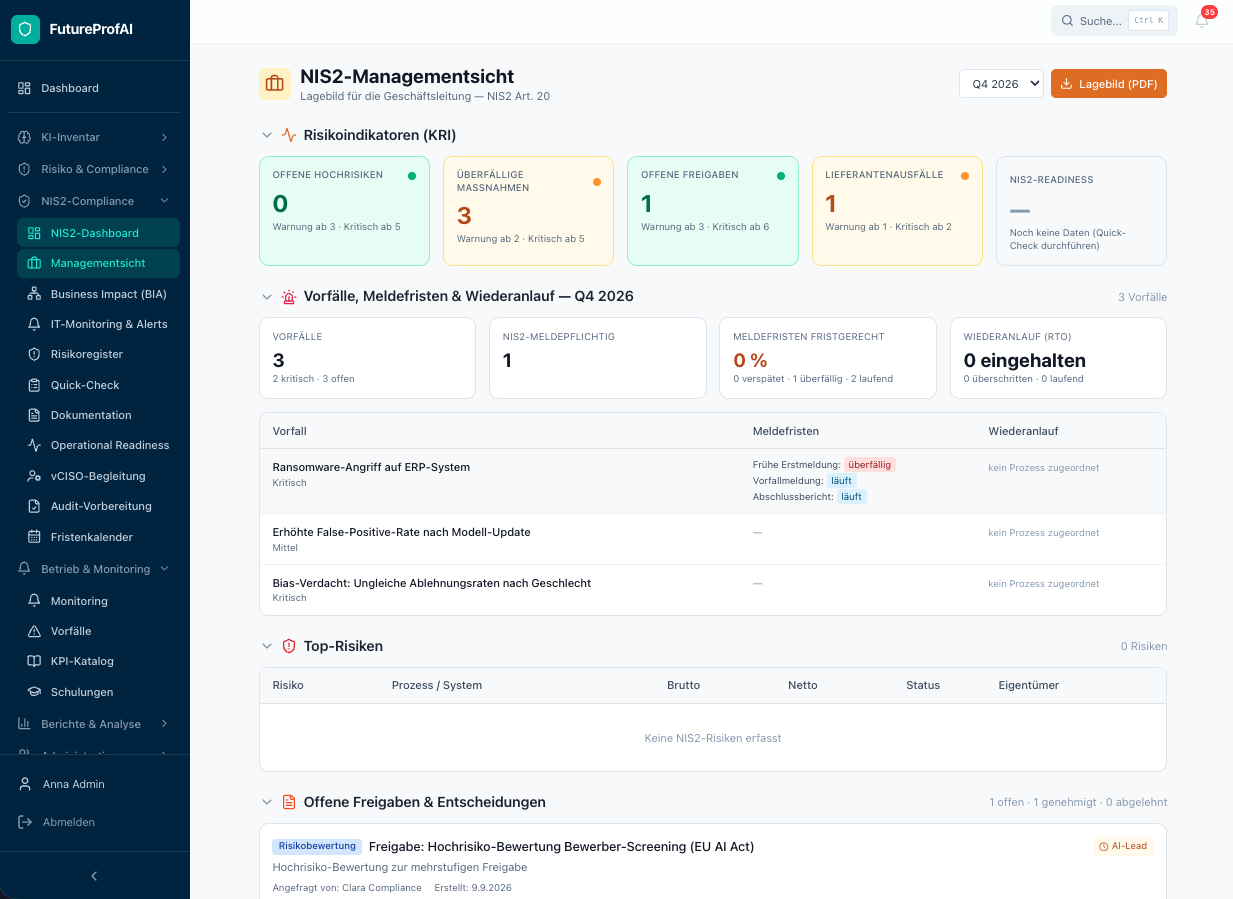
One module for AI governance and one for NIS2 on a shared foundation – from inventory or applicability to the report for management.
Consulting and software – not just a tool
Software alone does not implement compliance, and consulting alone often ends with documents nobody maintains. We combine both: consultants implement with you, the software keeps everything up to date.
Implementation with consultants
We build the inventory, risk assessment and mandatory documents together with your team – even without your own compliance or security department.
- Fixed-price packages with a clear scope
- One dedicated point of contact
- Results directly in the software
Evidence that stays alive
Instead of static documents, you work in software where systems, risks, controls and evidence are linked.
- The evidence chain shows gaps instantly
- Audit report as PDF
- Audit log for every change
Support when you need it
No new engagement needed after the project. Ongoing support is available as a predictable retainer.
- SCALE: managed AI governance
- vCISO support for NIS2
- Fixed monthly hour packages
Start small – no big project required
Three entry points with a clear price and a short duration. Afterwards you decide how to proceed.
Two regulations, one shared foundation
The EU AI Act and NIS2 remain separate topics with their own requirements. In five areas, however, you build on the same structures – and avoid duplicate effort.
In the software, the evidence chain connects both regulations: controls for NIS2 and the EU AI Act cross-reference each other, and one piece of evidence can be assigned to several requirements. See the evidence chain
Both from a single source: aligned packages, one point of contact, no duplicate workshops.
Request combined consultingFrom full service to self-service
We meet you where you are – and guide you systematically towards independent AI governance.
Full Consulting
Full ServiceMaximum hand-holding. We take over the complete capture and documentation of your AI governance.
- Complete as-is analysis by our consultants
- AI inventory capture & risk assessment
- Creation of all compliance documents
- Management report & recommended actions
Ideal for: Companies without internal AI governance resources
Managed Service
HybridInitial capture by us plus recurring data maintenance – you focus on your core business.
- Initial capture & software setup
- Ongoing maintenance by FutureProfAI
- Quarterly reviews & reports
- Dedicated point of contact
Ideal for: Companies that want to outsource AI governance
SaaS + Enablement
HandoverWe enable your team to use the software independently – with training and support.
- Software setup & configuration
- Hands-on training for your team
- Support during the transition phase
- Full software access & support
Ideal for: Companies with their own compliance team
Pure SaaS
Self-ServiceSelf-service software access with AI-assisted onboarding – maximum autonomy.
- Instant software access
- AI onboarding assistant
- All modules included
- Automatic updates & community support
Ideal for: Tech-savvy companies with AI governance experience
Industry-specific add-ons
Our core governance model, extended with industry-specific requirements, artefacts and review criteria.
Software & SaaS
For providers and deployers: customer impact sheets, release management, tenant isolation, API security.
MedTech & Health IT
Safety-first approach with QMS integration. Distinction between admin AI and product/patient-facing AI.
Insurance & B2B Services
Fairness, evidence and control focus for scoring, underwriting and fraud detection.
Construction & Real Estate
IP and project risk focus. Protection of sensitive calculations and construction project data.
Governance without Big4 overhead
Productised AI governance specifically for larger mid-sized companies – risk-based, EU AI Act-ready, fixed-price capable.
Transparent fixed prices
Clear cost structure from EUR 12k to 30k to get started. No surprises, no hourly-rate discussions.
Fast results
First results in 2-4 weeks. Productised packages instead of months of analysis phases.
Ready-made templates for evidence
15 templates (T1–T15) for risk-based evidence – from use-case one-pager via model card and incident log to the decommissioning checklist.
Legal validation
Optional: legal plausibility checks by partner law firms for critical classifications and contracts.
ISO/IEC 42001 ready
Governance model compatible with international AI Management System standards.
Mid-market DNA
Pragmatic solutions without Big4 overhead. "As much governance as needed, as little as possible."
Strong partners for full coverage
FutureProfAI delivers governance design and methodology. For legal validation and technical implementation we work with specialised partners.
Partner law firms
Legal Validation Partner
Legal plausibility checks of critical governance decisions by specialised law firms.
- EU AI Act classification review
- Vendor/DPA contract review
- GDPR compliance validation
- Provider/deployer role clarity
Implementation
Technology Partner
Technical implementation of governance requirements by experienced IT service providers.
- GenAI guardrails & security
- Logging & monitoring setup
- CI/CD quality gate integration
- Tool & platform selection
Interested in a partnership?
Are you a law firm, IT service provider or system house and want to offer your clients professional AI governance? Let’s talk.
Request a partnershipStart your AI governance journey
Book a free 30-minute risk triage and find out how to operate your AI systems safely and compliantly.
...or talk to us
Whether a quick question or comprehensive consulting – we’re here for you. Fill in the form and we’ll get back to you within 24 hours.